ASD Essentials GRC Compliance Platform

integrity-sm

100s of hours

Saved on compliance

collaboration

54%

Less compliance costs

innovation

12 weeks

To get certified

Make ASD Essentials part of how your organisation works

ASD has moved on from the Essential Eight, and the way your cyber security is measured has changed with it. de.iterate helps you implement, assess and evidence ASD Essentials in one integrated platform, with your policies, risks, assets, suppliers, evidence and assessments all connected.

Under the Essential Eight, a maturity level could tell you which box you'd ticked. ASD Essentials asks a harder question: does each control actually protect you, and can you prove it? Every action is rated on the evidence behind it. The weakest rating counts, and if you can't show evidence, the action isn't assessed at all. 

That's tough to manage with spreadsheets and shared folders. de.iterate turns it into a steady, repeatable way of working, so your ratings reflect what's really happening and your evidence is ready when someone asks for it.

how-deiterate-simplifies-compliance-blog-newsletter

What are the ASD Essentials?

ASD Essentials is the Australian Signals Directorate's cyber security framework, published on 15 October 2026 as the evolution of the Essential Eight. ASD designed it for Commonwealth entities, critical infrastructure owners and operators, and large organisations, though any organisation can use it.

Instead of eight mitigation strategies scored against maturity levels, ASD Essentials sets out principles and actions across eight domains. Six domains cover your technology, from Boundary Services and Identity Services through to Business Systems and User Devices. The other two, Governance and Culture and Visibility and Response, apply across everything you do. 

The framework comes in chapters, each written for a different technology environment, with supporting guides for transitioning, planning and assessing. ASD also recommends a sequence of priority phases, so you know where to start.

Done well, ASD Essentials gives your executives, your board and your customers a clear, evidence-based view of how well your cyber security is working.
deiterate-platform

What is de.iterate?

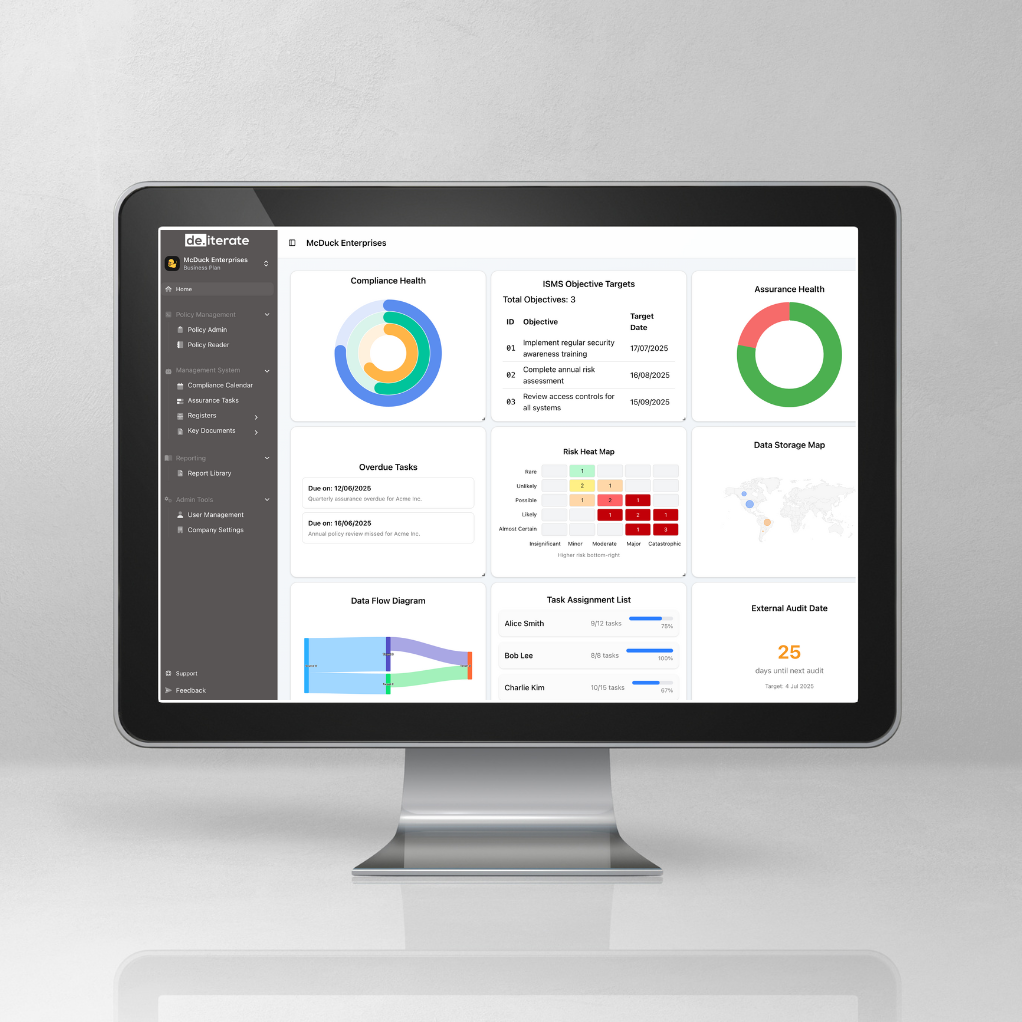
de.iterate makes ASD Essentials simpler, clearer and easier to sustain.

In place of Word documents, spreadsheets, shared folders and manual reminders, you get one integrated platform for your whole management system. Policies, training, risk registers, asset registers, supplier records, evidence, assurance tasks, audits and reporting all sit in one place, connected to each other and kept current.

Your evidence links to the right controls, risks and assets, so you can see what's behind every rating. Your policies reflect how your business actually works. And when the next assessment comes around, you're updating a living system, with nothing to rebuild.
risk-register-mock-up

Which ASD Essentials chapter do you need?

ASD Essentials for enterprise IT: the direct evolution of the Essential Eight, and the chapter most organisations will start with.

ASD Essentials for cloud: for organisations that run entirely on software as a service (SaaS) and platform as a service (PaaS).

ASD Essentials for OT: for critical infrastructure operators protecting operational technology environments.

Many organisations run a mix of environments. Our Aussie GRC experts can help you work out where to start.

Benefits of ASD Essentials with de.iterate

A lot of compliance tools help you collect activity. de.iterate helps you build assurance.

de.iterate delivers modern, scalable governance in a simple, plain-language platform that fits your business — not the other way around.

More than a checklist. More than automation. de.iterate delivers real governance programs that connect risk, compliance, privacy, safety, quality, and environmental management,  all in one place. We make governance and compliance easy in a plain-language, scalable platform that keeps your business in control, audit-ready, and confident every day.
integrity-sm

Carry your Essential Eight work across

You've already done a lot of the work. de.iterate maps your existing controls and evidence across to ASD Essentials, so you can see what still counts and focus on the gaps.
collaboration

Evidence that stands up to the new ratings

Every action is rated on its evidence. The Evidence Store links each piece of evidence to the control and requirement it supports, and Assurance Tasks keep it current, so fewer actions end up rated not assessed.

innovation

Scale your compliance with confidence

Extend your program into ISO 27001, ISO 42001, SOC 2 and other frameworks without starting from scratch. Controls are mapped across frameworks, so evidence collected once counts wherever it applies.

multiple-frameworks

Governance that's built in

ASD Essentials puts executive accountability, AI accountability and supplier assurance squarely in scope. de.iterate already manages your governance documents, supplier register and AI governance in the same platform, so the Governance and culture domain doesn't need a separate project.

harold-quackmore

Work through the priority phases

Plan your uplift phase by phase, starting with Boundary services and Identity services. Assign owners, track progress and show your executives where you're up to on custom dashboards.

migrate-faster

Migrate quickly & easily

Moving to a better compliance platform shouldn’t mean rebuilding your entire management system. de.iterate’s Management System Migration Tool helps you bring across existing policies, registers and supporting documentation from legacy systems, so you can transition faster and preserve the work you’ve already done.

Everything you need to run and prove compliance

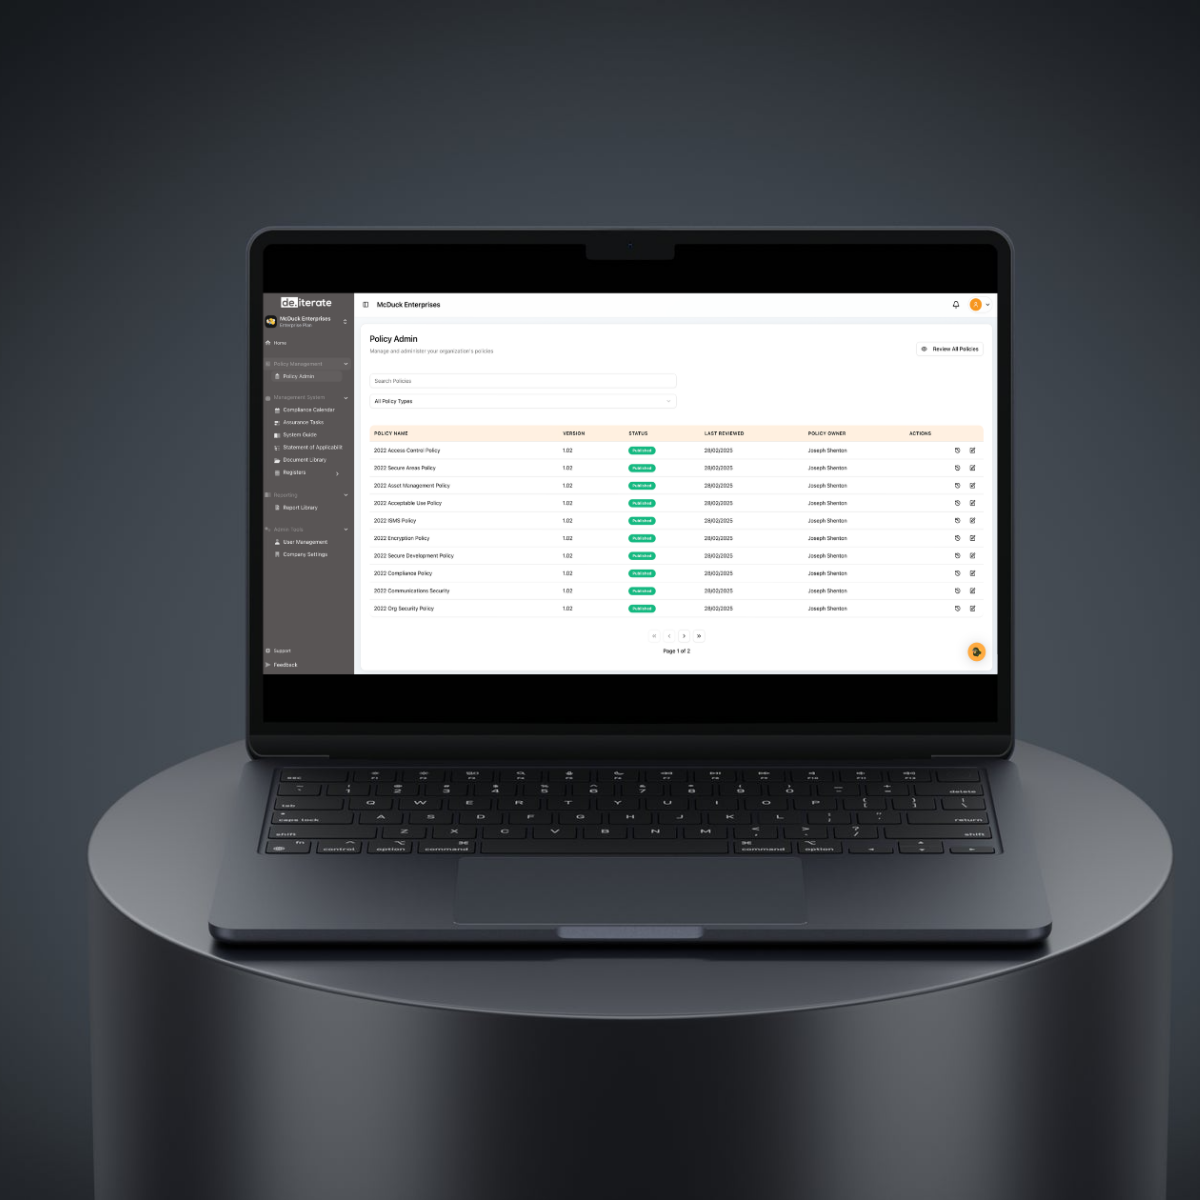
Governance and policy management

Create, approve and distribute plain-English policies, with version control and attestation evidence for every person and policy. Keep the documents that support executive accountability current and connected to the controls they cover.

Assurance and evidence

Turn ASD Essentials into scheduled Assurance Tasks, control self-assessments and checklists, each with an owner and a due date. Store evidence against the right control, track findings and corrective actions in the Audit Centre, and export evidence when your assessor asks for it.

Risks, assets and suppliers

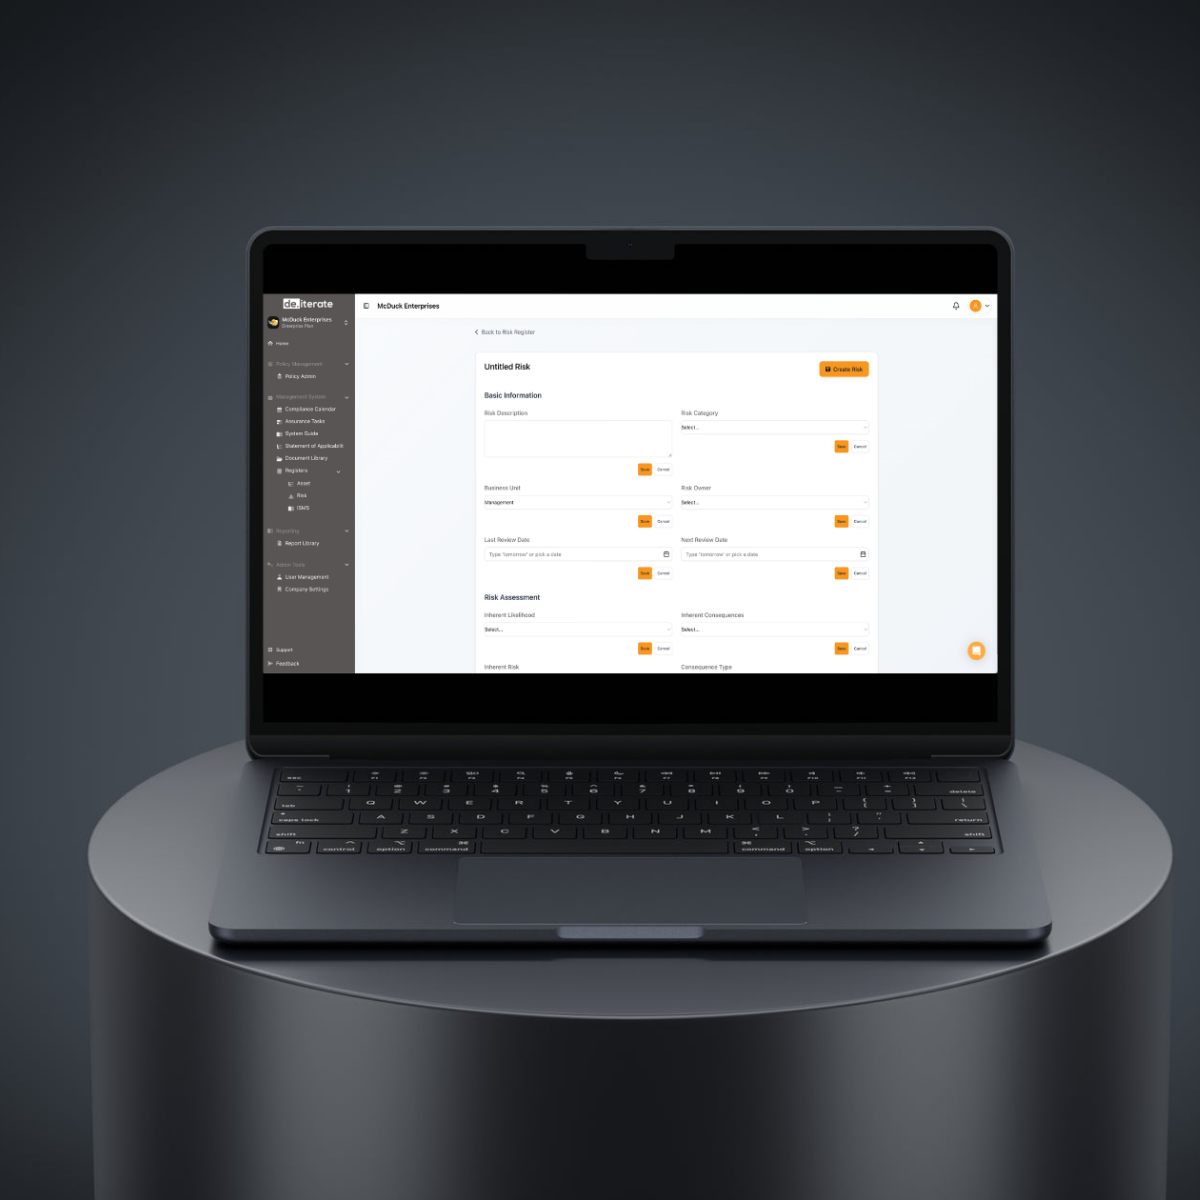
Manage what matters most to your organisation through our embedded risk management approach, with a risk, asset and supplier register. Bring all your scope, ownership, treatment plans, classifications and review cycles together in one easy-to-use platform.

policy-calendar

Automation where it helps. Context where it matters.

Plenty of platforms promise automation. de.iterate goes further by making that automation useful.

Every piece of evidence connects to the right control, risk, asset and process, so you know what each rating rests on. AI can map your existing documents to controls and suggest assurance tasks, and every suggestion arrives as a draft for a person to approve. That keeps your ratings honest, which is exactly what ASD Essentials asks for.


That is the difference between a tool that creates activity and a platform that creates assurance.

Frequently Asked Questions

Got questions? Luckily, we've got answers!

After all, we're here to help you get your ducks in a row.

What are the ASD Essentials?

ASD Essentials is the Australian Signals Directorate's cyber security framework, published on 15 October 2026 as the evolution of the Essential Eight. It sets out principles and actions across eight domains, in chapters written for enterprise IT, cloud and operational technology.

Do the ASD Essentials replace the Essential Eight?

ASD describes ASD Essentials for enterprise IT as the evolution of the Essential Eight. Both frameworks stay on cyber.gov.au during the transition, and no retirement date for the Essential Eight has been published. Keep meeting any obligation that names the Essential Eight until your regulator or contract says otherwise.

Do Essential Eight maturity levels carry across to the ASD Essentials?

No. ASD Essentials doesn't use maturity levels, and Essential Eight maturity levels don't convert into ASD Essentials ratings. Your existing controls and evidence still count, though, because every Essential Eight strategy maps to at least one part of ASD Essentials.

How are the ASD Essentials assessed?

Each action is rated not assessed, not effective, partially effective or fully effective, based on the evidence behind it. The lowest rating governs, and if there's no evidence, the action is rated not assessed. ASD's Assessment process guide explains the process.

Which ADS Essentials chapter should we use?

Most organisations start with ASD Essentials for enterprise IT. Organisations running entirely on SaaS and PaaS use the cloud chapter, and critical infrastructure operators use the OT chapter for their operational technology. ASD's Which chapter should I start with? paper helps if you run a mix.

Can I be certified to ASD Essentials?

If we could, we would. But there's no ASD Essentials certification. ASD's assessment guidance is written for self-assessment, and de.iterate gives you the evidence to back up your ratings when customers, insurers or regulators ask.

Can we run ASD Essentials and the Essential Eight side by side?

Yes. Controls in de.iterate are mapped across frameworks, so you can keep reporting against the Essential Eight where you need to while you move to ASD Essentials.

Simple monthly pricing, based on the frameworks you need

de.iterate pricing is structured around the compliance frameworks you choose to access, giving you the flexibility to build a program that fits your organisation’s needs. Every plan includes access to the de.iterate platform and its feature set, from automated and expert-led onboarding, through to migration support, assurance workflows, live registers, compliance reporting and the core documentation needed to run and maintain your management system with confidence.
AUD
GBP
Starter (per month)

$179£100

  • Essential Eight

  • SMB 1001

  • Privacy Acts

  • DISP

  • Cyber Essentials

Business (per month)

$2,100£1,250

  • ISO 27001

  • ISO 27701

  • ISO 42001

  • ISO 9001

  • ISO 45001

  • ISO 14001

  • SOC 2

  • NIST CSF 2.0

  • NIST 800-53

  • NIST 800-171

  • NIST 800-172

  • GDPR

  • Essential Eight

  • ASD Essentials

  • SMB 1001

  • Privacy Acts

  • DISP

  • Cyber Essentials

  • DORA

  • NIS2

  • CIS v8

  • EU AI Act

Enterprise (per month)

$3,500£2,000

  • ISO 27001

  • ISO 27701

  • ISO 42001

  • ISO 9001

  • ISO 45001

  • ISO 14001

  • SOC 2

  • NIST CSF 2.0

  • NIST 800-53

  • NIST 800-171

  • NIST 800-172

  • GDPR

  • Essential Eight

  • SMB 1001

  • Privacy Acts

  • DISP

  • ISM

  • SOCI

  • Right Fit for Risk (RFFR)

  • Cyber Essentials

  • DORA

  • NIS2

  • CIS v8

  • EU AI Act

  • TISAX

  • ASD Essentials

Ready for simple, stress-free compliance? Want help from real GRC experts?