Integrations & APIs

Connect your tools to de.iterate

Connect de.iterate to the tools you already use, and keep your compliance, governance and risk management evidence current without the copying and pasting.

Your policies live in SharePoint or Confluence. Your devices are managed in Intune or Jamf. Your team signs in through your identity provider. de.iterate connects to all of them, so your compliance, governance and risk management system reflects what's really happening in your business.

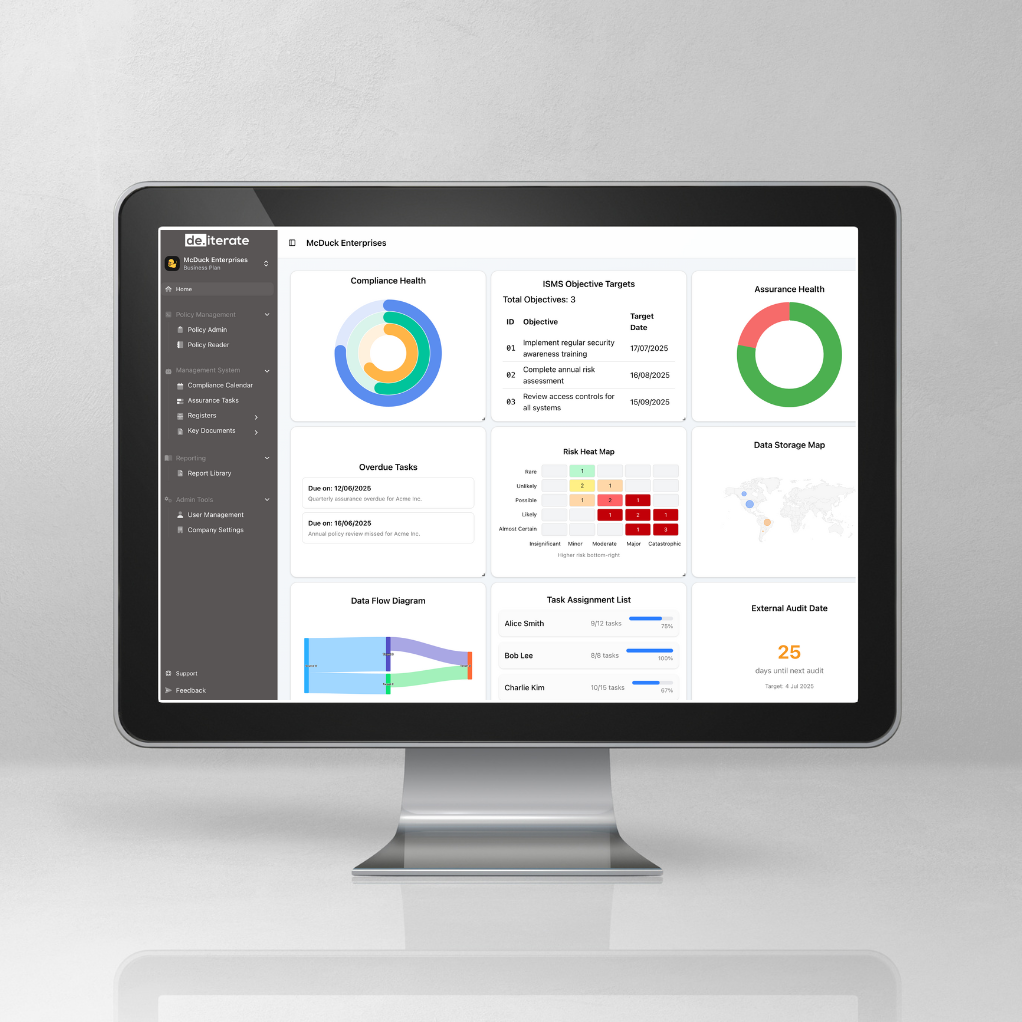
de.iterate is an Australian GRC platform built as one integrated management system (IMS). Every feature in de.iterate runs on the same platform. Risks, controls, obligations, policies, assets, suppliers, audits and evidence all link to each other, so a change in one place shows up everywhere it matters.

We help you get your ducks in a row.
deiterate-platform
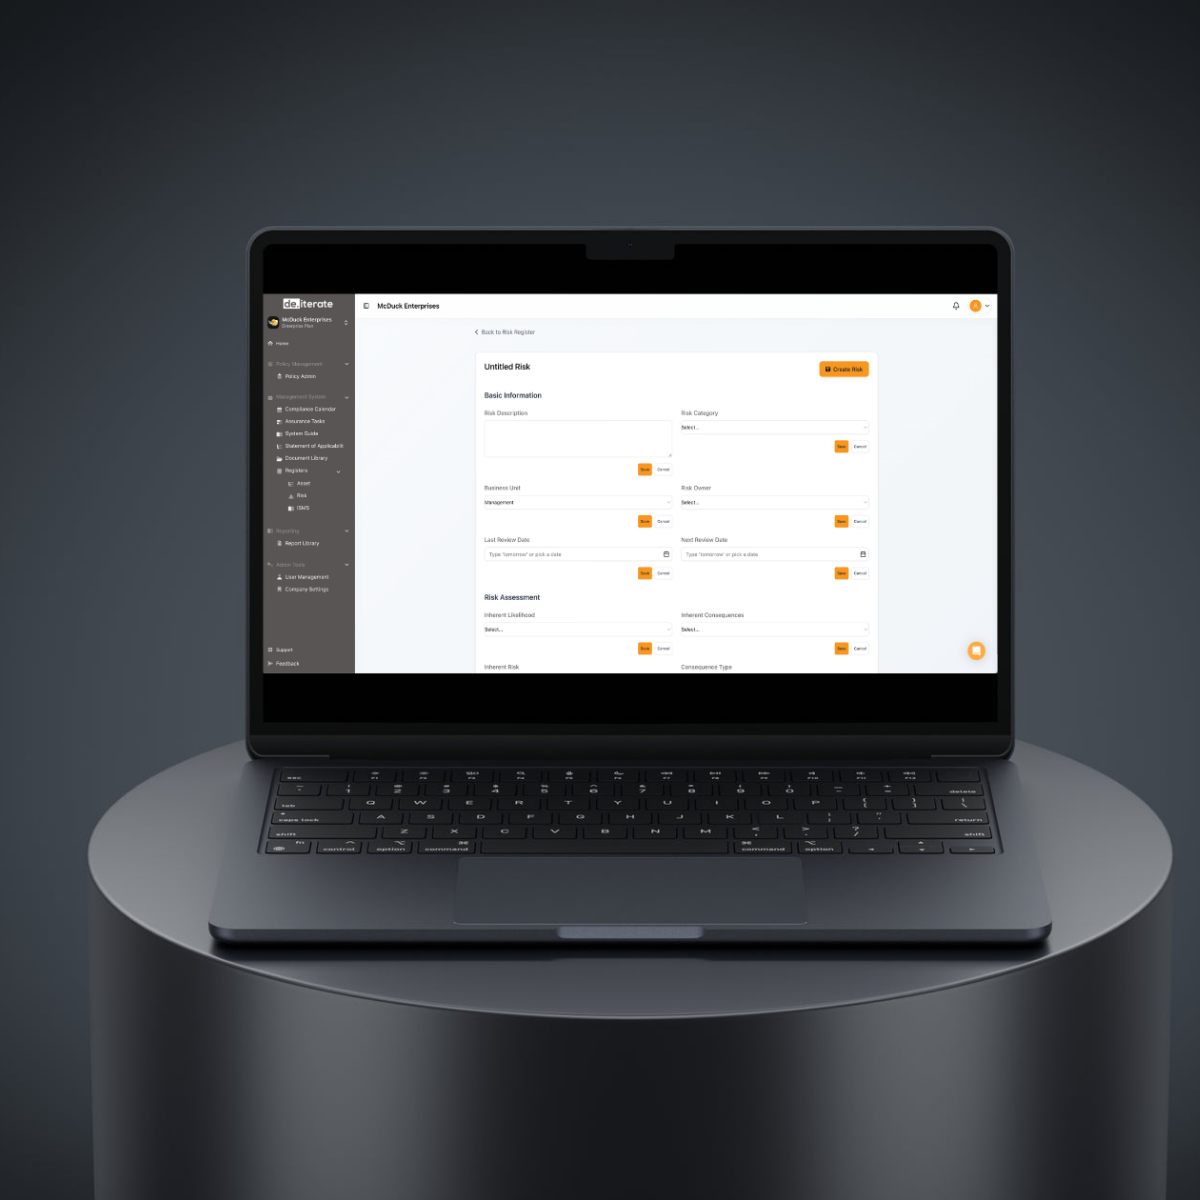
risk-register-mock-up

Copy, paste, screenshot, repeat

Most of the evidence your auditor wants already exists somewhere else. It’s in your device management tool, your document library and your identity provider. Getting it into your compliance program usually means someone taking screenshots, exporting spreadsheets and uploading files, then doing it all again next quarter.

de.iterate connects to those tools directly. Device compliance comes in from Intune, Jamf, CrowdStrike, Defender or SentinelOne, documents from SharePoint and Confluence, and users from Entra ID, each attached to the control it evidences and refreshed on a schedule you set. The screenshot stops being a task on someone’s list and becomes a feed, and when a source drifts out of tolerance de.iterate raises a finding rather than waiting for the next audit to notice.

Every manual step is a chance for something to go out of date. In de.iterate, the picture stays current because the systems that hold the evidence are the ones keeping it.
de.iterate's integrations

de.iterate connects to the systems that hold your governance and risk evidence, so controls are checked against live data, KRIs move on their own and the screenshot stops being someone’s job.

documents-knowledge

Documents & knowledge sharing

SharePoint · OneDrive · Confluence · Notion · Box · Dropbox · Google Drive

Keep policies and evidence where your team already works. de.iterate stays in sync with your document store, tracks review dates and approvals, and flags a policy that changed at the source without being re-approved. No second copy to maintain.

identity-access

Identity & access

Microsoft Entra ID · Okta · Ping Identity · Google Workspace · SailPoint · CyberArk · 1Password · SAML · OpenID Connect

Staff sign in with single sign-on and users sync from your identity provider. de.iterate then checks what the directory says: who has MFA, which leavers still have active accounts, which guests nobody sponsored and whether privileged accounts are vaulted. Access reviews come with the evidence already attached.

endpoint-vulnerabilities

Endpoints & vulnerabilities

Microsoft Intune · Jamf · Tanium · ManageEngine Endpoint Central · CrowdStrike · Microsoft Defender · SentinelOne · Tenable · Qualys · Rapid7 · Snyk

de.iterate compares your asset register with the tools that manage and protect your devices, and raises a finding when they disagree: a laptop in Intune with no EDR agent, a sensor that stopped reporting, a critical vulnerability open past your patching window. Mystery laptops don’t stay mysterious for long.

cloud-network-backup

Cloud, network & backup

Amazon Web Services · Microsoft Azure · Google Cloud · Wiz · Fortinet · Veeam · Acronis

Cloud accounts, security posture findings and firewall firmware feed your asset register and your KRIs, so every account has an owner, every critical finding has an age, and every system that needs a backup has had one inside its recovery window.

security-monitoring

Security monitoring, email & training

Microsoft Sentinel · Splunk · Datadog · PagerDuty · Microsoft Purview · Varonis · Proofpoint · Mimecast · KnowBe4 · Cornerstone OnDemand

de.iterate logs sources that go quiet, incidents that take too long to close, phishing clicks, overdue training and sensitive files open to everyone all become KRIs on the risks they affect, with the evidence collected for the assurance task that asks about them.

tickets-work-chat

Tickets, work & chat

ServiceNow · Jira · Freshservice · Zendesk · Ivanti · BMC Helix · ManageEngine ServiceDesk Plus · TOPdesk · Asana · monday.com · Smartsheet · ClickUp · Slack · Microsoft Teams

Compliance work lands in the tool your teams already use. With de.iterate, a non-conformance becomes a ticket, closing the ticket closes the task, and approvals and KRI alerts arrive in Teams or Slack rather than in another inbox.

people-training

People & training

Workday · SAP SuccessFactors · Employment Hero · ELMO · BambooHR · HiBob · Oracle Fusion HCM · ADP · Cornerstone OnDemand · KnowBe4

Your HR system becomes the source of truth for who works here, in what role and from when to when. de.iterate checks leavers against every account they held, flags joiners who haven’t completed their training, and keeps the people register current without anyone retyping it.

suppliers-contracts

Suppliers, contracts & finance

Coupa · SAP Ariba · SAP S/4HANA · Oracle NetSuite · Microsoft Dynamics 365 · Salesforce · HubSpot · Docusign · Adobe Acrobat Sign · BitSight · SecurityScorecard · OneTrust · Archer

Procurement and finance systems show which suppliers you’re paying and which haven’t been assessed. Signed agreements attach themselves to the supplier record, security ratings move a KRI when a critical supplier’s score drops, and existing registers in OneTrust or Archer come across rather than being rebuilt.

automations-reporting

Automation & reporting

Zapier · Microsoft Power Automate · Workato · Make · n8n · MuleSoft · Boomi · Power BI · Snowflake · Google BigQuery

Through Zapier, de.iterate reaches 9,000+ apps: any tool can push a KRI value, attach evidence or react when a risk changes. Enterprise integration teams get the same triggers and actions through their own platform, and your risk, KRI and control data flows into the dashboards and warehouses the board already reads.

reporting

Professional services automation (for MSPs)

ConnectWise · HaloPSA · Autotask · NinjaOne

Managed service providers can keep client compliance work on track in the tools they already use to run their business. Find out more about our Partner Program.

ai-security

AI usage & security

Netskope · Check Point · Zscaler · Palo Alto Networks · Cisco · Cloudflare One · Microsoft Defender for Cloud Apps · Fortinet

See which AI apps your people are using, which ones nobody approved and whether sensitive data is going into prompts. These tools feed the shadow-AI KRIs and the evidence ISO 42001 asks for.

ai-agent

AI platforms & agents

ChatGPT Enterprise · Claude Enterprise · Microsoft Copilot Studio · Azure AI Foundry · Amazon Bedrock · Google Vertex AI · Salesforce Agentforce · Wiz

Keep your AI register current from the source. de.iterate reads the agents, models, connectors and MCP servers that exist inside each platform, flags the ones that aren’t registered or have write access without a risk assessment, and enriches each record with what the agent can touch.

The de.iterate API

Don't see your system above? Build your own connection with the de.iterate API.

connect-policy-obligation

Bring in data from your own systems

Connect in-house, on-premise or niche tools that don't have a native integration, and send their data straight into de.iterate as evidence.

policy-worth-reading

Take the busywork out of admin

Connect in-house, on-premise or niche tools that don't have a native integration, and send their data straight into de.iterate as evidence.

automations-reporting

Feed your own reporting

Pull data out of de.iterate and into your business intelligence or reporting tools, so compliance and risk sit alongside the rest of your management reporting.

genuinely-useful

Kick off workflows elsewhere

Use de.iterate data to trigger actions in your other systems, so a gap spotted in de.iterate can start a fix somewhere else.

secure-by-design

Secure by design

Granular role-based access control lets you decide exactly what each connection can read and change, and remove access whenever you need to. Your de.iterate data is hosted in Australia or the EU, in the jurisdiction you choose.

ai-responsibility

Move a KRI from any source

Send a measurement from any system, such as a count of unpatched servers from an in-house script or an overdue-review figure from a legacy tool, and de.iterate turns it into a key risk indicator. When the number crosses the threshold you set, the risk owner is alerted and corrective action starts, without a native connector in sight.

Frequently Asked Questions

Most questions about the platform itself come down to trust and fit: where your data lives, how de.iterate connects to what you already run, and what happens when you need help. The answers below cover the detail, from hosting to sign-on to the people on the other end of the chat.

Which integrations does de.iterate offer?

de.iterate connects with places like Zapier, SharePoint and Confluence, Microsoft Entra ID, single sign-on through SAML and OpenID Connect, endpoint tools such as Microsoft Intune, Jamf, CrowdStrike, Microsoft Defender and SentinelOne, and AI assistants via MCP. MSPs can also connect ConnectWise, HaloPSA, Autotask and NinjaOne.

What can we do with the de.iterate API?

Bring in data from systems that don't have a native integration, automate repetitive admin, pull data into your own reporting tools and trigger workflows in other systems.

How is access to the API controlled?

de.iterate has granular role-based access control that lets you decide what each connection can read and change. You can remove a connection's access at any time.

Can we connect Claude, ChatGPT or Gemini to de.iterate?

Yes. AI assistants connect to de.iterate via MCP, and role-based access control decides exactly what each one can see and do.

Is the API included in our plan?

Yes. The de.iterate API is included in all our plans.

Can we request a new integration?

Yes. Email support@deiterate.com and tell us which tool you'd like connected. Customer requests help us decide what to build next.

Where is our data stored?

de.iterate is hosted in Australia or the EU, in the jurisdiction you choose. Production, backups and disaster recovery all stay there.

Can we bring in data without an integration?

Yes. de.iterate's spreadsheet import wizard brings in risks, assets and suppliers, and our Management System Migration Tool moves your existing policies, registers and documents across.

What makes de.iterate different

From setup to scale, every feature is designed to help your team save time, stay focused, and drive meaningful results.

Expert support, not just software

de.iterate combines technology with hands-on support from experienced GRC professionals based in Australia. From onboarding through to certification, our team works with you to build momentum quickly, helping many organisations get audit-ready in less than 12 weeks and providing practical support through external audits and ongoing compliance activities.

Continuous compliance, not annual panic

Great compliance is not built in the two weeks before an audit. de.iterate helps you stay ready year-round with assurance tasks, checklists, live registers, reporting and a compliance calendar that keeps momentum going.

Practical enough to use, powerful enough to scale

From start-ups to enterprise, de.iterate supports multiple frameworks in one system, including ISO 27001, ISO 27701, ISO 9001, ISO 14001, ISO 45001, Privacy Acts, SOC 2, DIP, Essential Eight and more. You can grow your compliance maturity without rebuilding everything from scratch.

Key Features

A smarter way to manage compliance

de.iterate combines policies, training, registers, evidence, reporting and assurance workflows in one integrated management system, helping you reduce complexity, stay audit-ready and turn governance, risk management and compliance into business as usual. Every feature is designed to save time, strengthen accountability and make GRC compliance easier to manage across your organisation.
compliance-management

Enterprise Risk Management

 A risk register with a pulse, with inherent and residual scoring, heatmaps and risk appetite. 

board-reporting

Compliance Management

 Every obligation traced to the evidence that meets it, across 25+ frameworks.

policy-management

Policy Management

 Plain-English policies, clear approvals and proof your staff have read them. 

controls-management

Controls Management

 Scheduled controls testing, with the evidence ready before your auditor asks. 

supplier

Third Party Risk Management

Keep tabs on the suppliers holding a slice of your risk.

it-cyber-security-consultants

Cyber & IT Risk

 Your whole ISMS, from asset register to Statement of Applicability.

AI-gov

AI Governance

 ISO 42001, AI impact assessments and an inventory of the AI in your business. 

data-privacy

Privacy & Data Governance

 Find your personal information, see where it goes and keep your privacy policy current.

audit-management

Audit Management

 Audit programs, findings and corrective actions tracked to closure. 

Multiple compliance frameworks, without extra effort


With de.iterate, the complexity of managing multiple frameworks doesn’t translate into increased workload. Our unified platform serves as a central hub for overseeing all your compliance activities, whether you’re working with bespoke frameworks or seeking to meet the criteria of the most sought-after security and privacy standards and certifications.

ISO 27001

Information Security Management Systems

The international standard that sets out the requirements for data protection systems. It’s all about keeping data safe and secure.
ISO 9001

Quality Management Systems

This standard defines the requirements for quality management. It’s all about ensuring your business consistently delivers high-quality products and services.
ISO 45001

Occupational Health and Safety Management Systems

The standard that specifies the requirements for an effective OH&S management system. Create a safer, healthier workplace.
ISO 14001

Environmental Management Systems

The global standard for building EMS. It gives you a structure to identify environmental impacts, manage obligations, strengthen governance.

ISO 42001

Artificial Intelligence Management Systems

This standard specifies the requirements for managing AI systems responsibly and ethically. It helps ensure trustworthy development and use of AI.

SOC 2

System and Organisation Control 2

This specifies how organisations should manage their customer’s data. It is one of the most sought-after security framework for SaaS companies. 

Privacy Acts

Australia, New Zealand, Canada, France, Italy, US and UK

Country-specific legislative frameworks established to protect individuals’ personal information from misuse, interference, unauthorised access, modification, and disclosure.

RRFR

Right Fit for Risk

The Australian Government’s Department of Employment and Workplace Relations uses the External Systems Accreditation Framework and the RFFR approach to assess and accredit third party service providers and systems.

DISP

Defence Industry Security Program

DISP is a critical initiative that ensures businesses in the defence supply chain meet stringent security requirements. DISP compliance is essential for companies that engage in Defence tenders, contracts and projects.

Simple monthly pricing, based on the frameworks you need

de.iterate pricing is structured around the compliance frameworks you choose to access, giving you the flexibility to build a program that fits your organisation’s needs. Every plan includes access to the de.iterate platform and its feature set, from automated and expert-led onboarding, through to migration support, assurance workflows, live registers, compliance reporting and the core documentation needed to run and maintain your management system with confidence.

AUD
GBP
Starter (per month)

$179£100

  • Essential Eight

  • SMB 1001

  • Privacy Acts

  • DISP

  • Cyber Essentials

Business (per month)

$2,100£1,250

  • ISO 27001

  • ISO 27701

  • ISO 42001

  • ISO 9001

  • ISO 45001

  • ISO 14001

  • SOC 2

  • NIST CSF 2.0

  • NIST 800-53

  • NIST 800-172

  • NIST 800-172

  • GDPR

  • Essential Eight

  • SMB 1001

  • Privacy Acts

  • DISP

  • Cyber Essentials

  • DORA

  • NIS2

  • CIS v8

  • EU AI Act

  • TISAX

Enterprise (per month)

$3,500£2,000

  • ISO 27001

  • ISO 27701

  • ISO 42001

  • ISO 9001

  • ISO 45001

  • ISO 14001

  • SOC 2

  • NIST CSF 2.0

  • NIST 800-53

  • NIST 800-171

  • NIST 800-172

  • GDPR

  • Essential Eight

  • SMB 1001

  • Privacy Acts

  • DISP

  • ISM

  • SOCI

  • Right Fit for Risk (RFFR)

  • Cyber Essentials

  • DORA

  • NIS2

  • CIS c8

  • EU AI Act

  • TISAX

Less copying and pasting. More time for the work that matters.

Book a demo and we'll show you how de.iterate connects to the tools you already use.