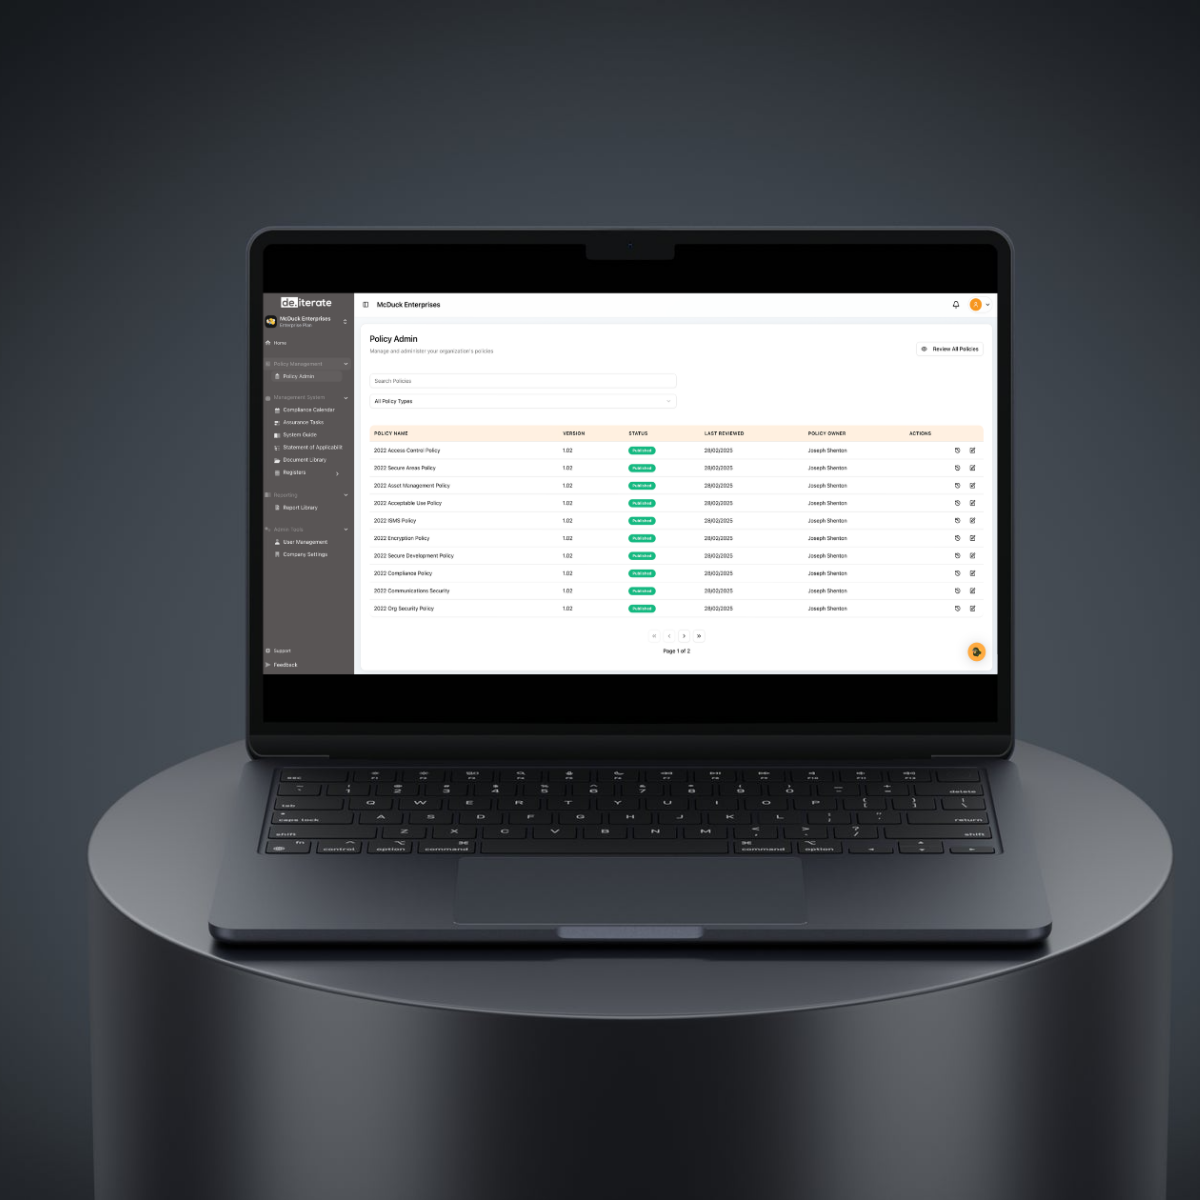
de.iterate is an Australian GRC platform with policy management built in. A policy only works if people know what's in it. de.iterate handles the whole policy lifecycle, from first draft to attestation, and our Smart Policies are written so your staff make it to the end.
Instead of managing policies in one place, risks in another, evidence in folders, and audits through a last-minute scramble, de.iterate connects the whole system. That means better visibility, clearer ownership, stronger assurance and less time lost to manual admin. The current platform spans policies, assurance tasks, registers, evidence, reporting, Trust Centre capabilities, auditor access and support for multiple frameworks.
We help you get your ducks in a row.
“Which version is current?”
“The one in the shared drive. No, the other shared drive.” Your acceptable use policy runs to 38 pages, and the only proof anyone read it is a tick box on an onboarding form from 2022.
Larger organisations have an intranet for this, and the problem has moved rather than gone. The policy library holds 140 documents across four business units and three countries, each with its own owner, its own review cycle and its own idea of what the acceptable use policy should say. Staff attested to a version in the annual campaign; the version was superseded two months later; the attestation records still say “complete.” Legal owns the register, HR owns the attestations and security owns the content, and the only person who can say which policies apply to a given employee is on leave.
When the auditor asks who approved the last change, the answer involves a lot of scrolling through old emails.
A policy only counts when there’s one current version, a record of who approved it, and proof that the people it applies to have read it since it last changed. de.iterate keeps all three in one place. Policies are written in plain English from expert templates, every change and approver is recorded, distribution matches the policy to the people who need it, and attestation includes evidence that it was read rather than clicked.
Tailor templates written by our GRC experts instead of starting from a blank page. Smart Policies explain your rules in plain English, ready for onboarding and ongoing training.
Route each policy for review and approval. The audit trail records every change and every approver, and the version-controlled repository keeps the full history.
Distribute policies to staff, contractors and third parties from the Admin Panel, or assign them to individuals. When a policy changes, reset its read status and everyone re-attests.
Reading reports from the Policy Reader include policy ‘dwell time’ so you can see who’s reading and who’s not. Results from policy quizzes become attestation evidence you can hand to your auditor. Use our template quizzes or write your own.
Set a review cycle for every policy and name its owner. de.iterate tracks the next review date, reminds the owner before it falls due, and flags anything overdue on the dashboard, so the auditor’s “when was this last reviewed?” has an answer with a date on it.
Link each policy to the controls it supports and the frameworks that require it. When an obligation changes, you can see which policies need updating, and when an auditor asks how you meet a clause, you can trace it from the standard to the policy to the people who attested to it.
Most questions about the policy module come down to two things: can we bring what we already have, and will an auditor accept what comes out. Yes to both. The answers below cover the detail, from importing your existing policies to proving they’ve been read.
Yes. Upload them and de.iterate's AI document ingestion maps them to your framework controls. Our Management System Migration Tool and team can bring across the rest.
Reading reports and quiz results from de.iterate's Policy Reader give you attestation evidence for each person and each policy.
Yes. de.iterate lets you build a custom framework or import your own, then map it to your existing controls.
Yes. de.iterate's template library is written by our GRC experts and covers the policies and documents each framework needs. Tailor them to your business and you're well on your way.
Yes. de.iterate's approval workflows route each policy to the right reviewers and approvers, and the audit trail records every change and every sign-off.
Yes. de.iterate's Admin Panel distributes policies to staff, contractors and third parties, and you can assign policies to individuals.
de.iterate saves the new version. You can then reset the policy's read status, so everyone reads and attests to the new version.
From setup to scale, every feature is designed to help your team save time, stay focused, and drive meaningful results.
de.iterate combines technology with hands-on support from experienced GRC professionals based in Australia. From onboarding through to certification, our team works with you to build momentum quickly, helping many organisations get audit-ready in less than 12 weeks and providing practical support through external audits and ongoing compliance activities.
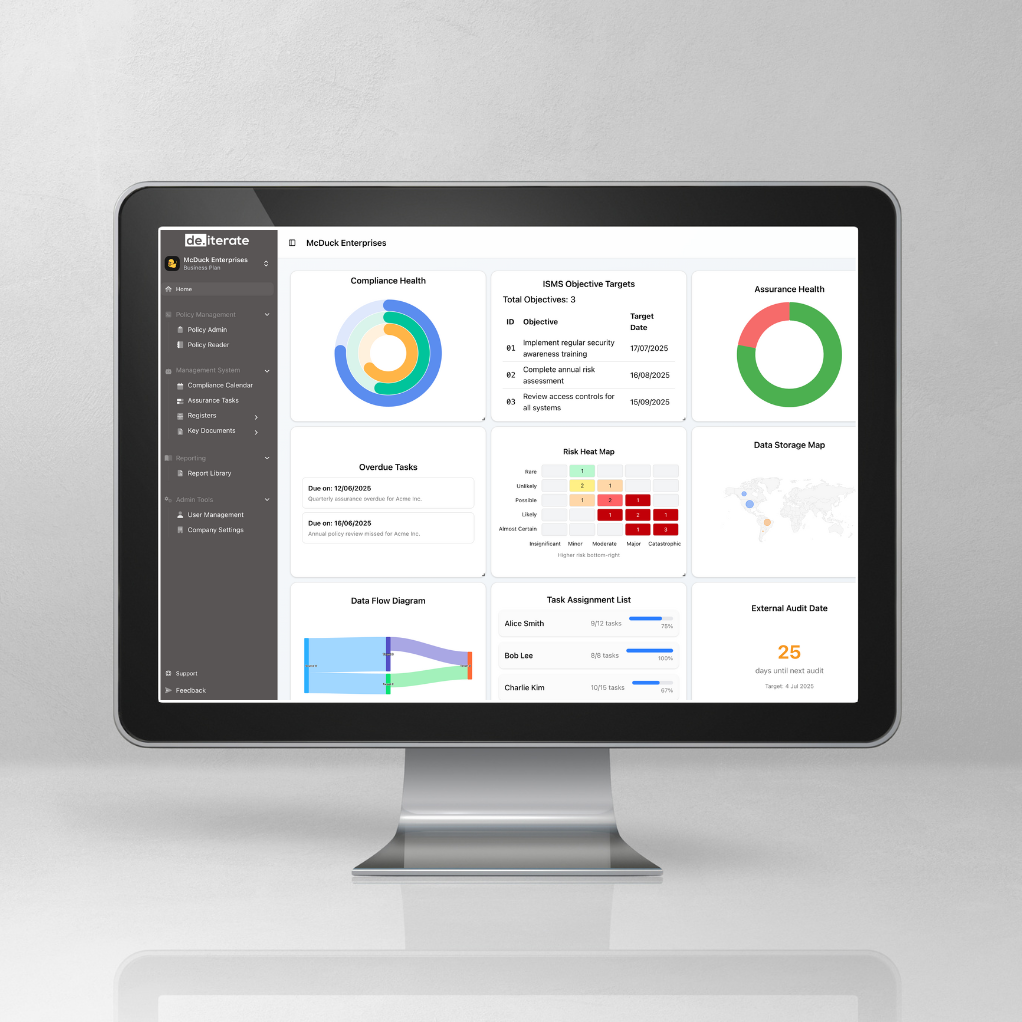
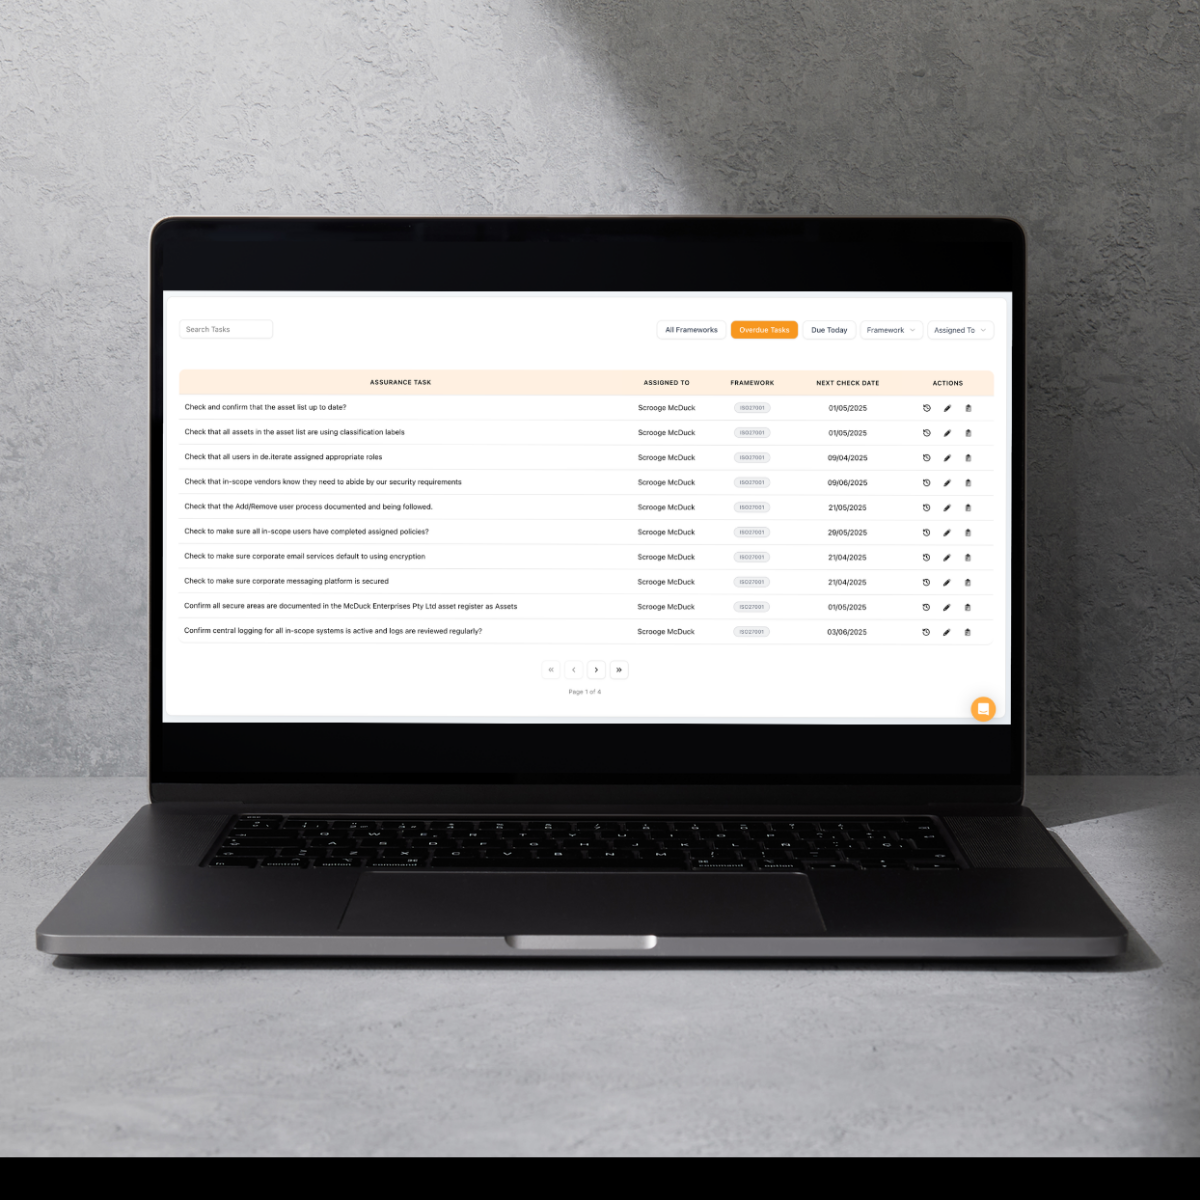
Great compliance is not built in the two weeks before an audit. de.iterate helps you stay ready year-round with assurance tasks, checklists, live registers, reporting and a compliance calendar that keeps momentum going.
From start-ups to enterprise, de.iterate supports multiple frameworks in one system, including ISO 27001, ISO 27701, ISO 9001, ISO 14001, ISO 45001, Privacy Acts, SOC 2, DIP, Essential Eight and more. You can grow your compliance maturity without rebuilding everything from scratch.
Many tools stop at storage. de.iterate goes further by connecting your policies, controls, evidence, registers and assurance activity in context. That means your documentation is not just centralised, it is structured, linked and easier to defend.
We believe compliance should be simpler, clearer and more achievable. That is why de.iterate combines structured workflows, smart documentation, migration support and guided onboarding with a platform that is intuitive enough for teams to use every day.
de.iterate is designed for the way organisations actually work. Policies, risks, assets, incidents, suppliers, evidence, audits and reporting all sit in one integrated platform, so compliance becomes part of business as usual.
A risk register with a pulse, with inherent and residual scoring, heatmaps and risk appetite.
Every obligation traced to the evidence that meets it, across 25+ frameworks.
Scheduled controls testing, with the evidence ready before your auditor asks.
ISO 42001, AI impact assessments and an inventory of the AI in your business.
Find your personal information, see where it goes and keep your privacy policy current.
ISO 9001, ISO 14001 and ISO 45001, running alongside everything else you manage.
With de.iterate, the complexity of managing multiple frameworks doesn’t translate into increased workload. Our unified platform serves as a central hub for overseeing all your compliance activities, whether you’re working with bespoke frameworks or seeking to meet the criteria of the most sought-after security and privacy standards and certifications.
The global standard for building EMS. It gives you a structure to identify environmental impacts, manage obligations, strengthen governance.
This standard specifies the requirements for managing AI systems responsibly and ethically. It helps ensure trustworthy development and use of AI.
This specifies how organisations should manage their customer’s data. It is one of the most sought-after security framework for SaaS companies.
Country-specific legislative frameworks established to protect individuals’ personal information from misuse, interference, unauthorised access, modification, and disclosure.
The Australian Government’s Department of Employment and Workplace Relations uses the External Systems Accreditation Framework and the RFFR approach to assess and accredit third party service providers and systems.
DISP is a critical initiative that ensures businesses in the defence supply chain meet stringent security requirements. DISP compliance is essential for companies that engage in Defence tenders, contracts and projects.
de.iterate pricing is structured around the compliance frameworks you choose to access, giving you the flexibility to build a program that fits your organisation’s needs. Every plan includes access to the de.iterate platform and its feature set, from automated and expert-led onboarding, through to migration support, assurance workflows, live registers, compliance reporting and the core documentation needed to run and maintain your management system with confidence.
Essential Eight
SMB 1001
Privacy Acts
DISP
Cyber Essentials
ISO 27001
ISO 27701
ISO 42001
ISO 9001
ISO 45001
ISO 14001
SOC 2
NIST CSF 2.0
NIST 800-53
NIST 800-172
NIST 800-172
GDPR
Essential Eight
SMB 1001
Privacy Acts
DISP
Cyber Essentials
DORA
NIS2
CIS v8
EU AI Act
TISAX
ISO 27001
ISO 27701
ISO 42001
ISO 9001
ISO 45001
ISO 14001
SOC 2
NIST CSF 2.0
NIST 800-53
NIST 800-171
NIST 800-172
GDPR
Essential Eight
SMB 1001
Privacy Acts
DISP
ISM
SOCI
Right Fit for Risk (RFFR)
Cyber Essentials
DORA
NIS2
CIS c8
EU AI Act
TISAX
We'll take a policy from draft to signed off in your demo, so you can see every step.