
ASD Essentials: Where to start
How to add ASD Essentials to your existing Essential Eight or ISO 27001 compliance program
In our last post, ASD Essentials is here, we covered what ASD Essentials is and how it's structured. Now for the question we're hearing most: we've already done the work, so what happens to it?
Good news first. Whether you've built your program around the Essential Eight, ISO 27001 or both, you're not starting from zero. You'll need to look at your work through a new lens, though, and there's some genuinely new ground to cover.
Let's take each starting point in turn.
Part 1: Moving from the Essential Eight
What carries across
ASD's Transitioning from the Essential Eight guide maps every Essential Eight strategy to at least one principle in ASD Essentials for enterprise IT. ASD's FAQ says that in most cases, controls you built for the Essential Eight will directly satisfy, or substantially contribute to, a corresponding action. Here's roughly where each strategy lands:
|
Essential Eight strategy |
Where it lands in ASD Essentials |
|
Application control |
Trustworthy software; Secure configuration management |
|
Patch applications |
Vulnerability management; Asset identification; Legacy system management |
|
Patch operating systems |
Vulnerability management; Asset identification; Legacy system management |
|
Multi-factor authentication |
Identity, credential and access management |
|
Restrict administrative privileges |
Identity, credential and access management; Least privilege access; Secure administration; Network segmentation and segregation |
|
Restrict Microsoft Office macros |
Trustworthy software; Secure configuration management |
|
User application hardening |
Secure configuration management |
|
Regular backups |
Regular and proven backups; Least privilege access |
Notice that the principles are broader than the strategies. Patching, for example, becomes risk-based vulnerability management, and macro restrictions now feed into a wider outcome about whether all your software can be trusted.
What doesn't carry across
Your maturity level. Sorry.
Essential Eight maturity levels and ASD Essentials ratings measure different things, so there's no conversion. A Maturity Level Two result becomes the starting point for a gap analysis, not a rating. You'll need to assess each action in each domain, and show the evidence behind it.
What's genuinely new
The Essential Eight never covered some areas that ASD Essentials now expects:
- Governance: executive accountability, cyber security resourcing, supplier assurance, AI accountability and legacy systems
- Asset and risk identification: a current inventory of your infrastructure, applications, identities, credentials and data
- New protections: content filtering, cyber security awareness training and supply chain security
- Visibility and response: logging, detection and incident response, now in their own domain
ASD also raises the bar on some familiar controls. For example, advisory firms reviewing the implementation guidance report that SMS, voice or push-only multi-factor authentication is rated not effective, and standing privileged access is too (break-glass accounts aside). If your Essential Eight program leaned on either, put them near the top of your list.
ASD's six transition steps
ASD recommends following this sequence:
- Establish a transition baseline. Record where you are today: your latest Essential Eight results, existing controls, exceptions, risk registers, remediation plans and committed work.
- Scope the phase 1 domains. Map your assets and business functions to Boundary services, Identity services, Governance and culture, and Visibility and response. Reuse your existing asset inventories and business impact assessments.
- Run a gap analysis. For each action, mark whether it's already addressed, partially addressed or not addressed, and note how your existing controls contribute.
- Plan the work. Fix gaps that affect one domain where they sit. Build shared capabilities, such as logging or identity, once and roll them out in phase order.
- Deliver and measure. As controls land, gather evidence of coverage, consistency, currency and quality.
- Move through the phases. Progress to phase 2 and phase 3 domains, and set a regular reassessment cycle.
Should you stop your Essential Eight program?
No. ASD says to keep approved uplift programs running while you check them against the new framework. Map your planned work to ASD Essentials actions before deciding whether it carries on unchanged. ASD also advises against starting new work purely to hit a superseded Essential Eight target, unless a regulator, contract or real risk still needs it.
And if your tender, insurance policy or contract asks for an Essential Eight maturity level, keep reporting it until they say otherwise.
Mistakes to avoid
ASD flags a few traps. These are the ones we'd underline:
- Treating priority phases as maturity levels. Phase 2 tells you where to work next. It doesn't say how secure you are.
- Claiming equivalence instead of assessing. "We were Maturity Level Two, so we're fine" won't survive an assessment.
- Leaving the capability domains until later. Governance and culture, and Visibility and response, apply from day one.
- Reusing stale evidence. Last year's screenshot is last year's screenshot.
Part 2: Adding ASD Essentials to your ISO 27001 program
If you run an ISO 27001 information security management system (ISMS), you're in a strong position, but for different reasons.
A quick note before we start: ASD hasn't published an official mapping between ASD Essentials and ISO 27001. What follows is our own guidance, based on how the two frameworks are built. We will also be publishing a detailed mapping resource. If you'd like a copy, subscribe to our newsletter.
Two frameworks that do different jobs
ISO 27001 is a management system standard. It asks you to understand your context, assess your risks, choose controls to treat them, and keep improving through internal audit and management review. You choose controls based on risk, and a certification body checks that your ISMS works as a system.
ASD Essentials is closer to a technical baseline. It tells you which outcomes to achieve, which actions to take, and in what order. Then it rates how effective each action is in each domain.
The two fit together nicely. ISO 27001 gives you the management system, and ASD Essentials tells you what good looks like for the technical controls inside it.
Where your ISMS gives you a head start
- Governance and culture. Leadership commitment, roles and responsibilities, risk assessment, internal audit and management review are all core ISO 27001 requirements. They give you a strong base for ASD Essentials' governance principles.
- Asset identification. Your Annex A asset inventory (control 5.9) gives you a starting point for scoping assets into domains.
- Supplier assurance. Annex A controls 5.19 to 5.23 cover supplier relationships and cloud services, which line up with ASD Essentials' supplier and cloud expectations.
- Incident response. Annex A controls 5.24 to 5.28 give you incident management processes to build Visibility and response on.
- Technical controls. Controls such as 8.2 (privileged access rights), 8.5 (secure authentication), 8.8 (technical vulnerabilities), 8.13 (backups), 8.15 and 8.16 (logging and monitoring) and 8.22 (network segregation) all overlap with ASD Essentials actions.
Where you'll need to go further
- Specificity. ISO 27001 lets you decide how to implement a control based on your risk. ASD Essentials is more prescriptive about what effective looks like. Your MFA control might satisfy your auditor and still be rated not effective if it relies on SMS codes.
- Domain-by-domain assessment. An ISO 27001 audit samples your ISMS. ASD Essentials rates every action in every domain it applies to, so you'll need evidence for each.
- Proof of effectiveness over time. Your ISMS probably has good documentation. ASD Essentials wants operational evidence too, such as test results, monitoring records and restore tests.
How to bring ASD Essentials into your ISMS
- Add it to your obligations. Record ASD Essentials in your legal, regulatory and contractual register, and in your list of interested parties' requirements, where it applies to you.
- Map your Annex A controls to ASD Essentials actions. Note where a control fully covers an action, partly covers it or doesn't cover it at all.
- Update your risk treatment plan. Add the gaps as risk treatments, prioritised in ASD's phase order.
- Update your Statement of Applicability if new controls come into scope.
- Build ASD Essentials self-assessment into your internal audit program, so effectiveness ratings feed into your management review.
- Report by domain. Give your executives the domain view ASD recommends, alongside your usual ISMS reporting.
The best part? You don't need two programs. One ISMS can satisfy both, as long as your controls are mapped to both frameworks.
How de.iterate can help
Whichever framework you're coming from, de.iterate makes the move easier.
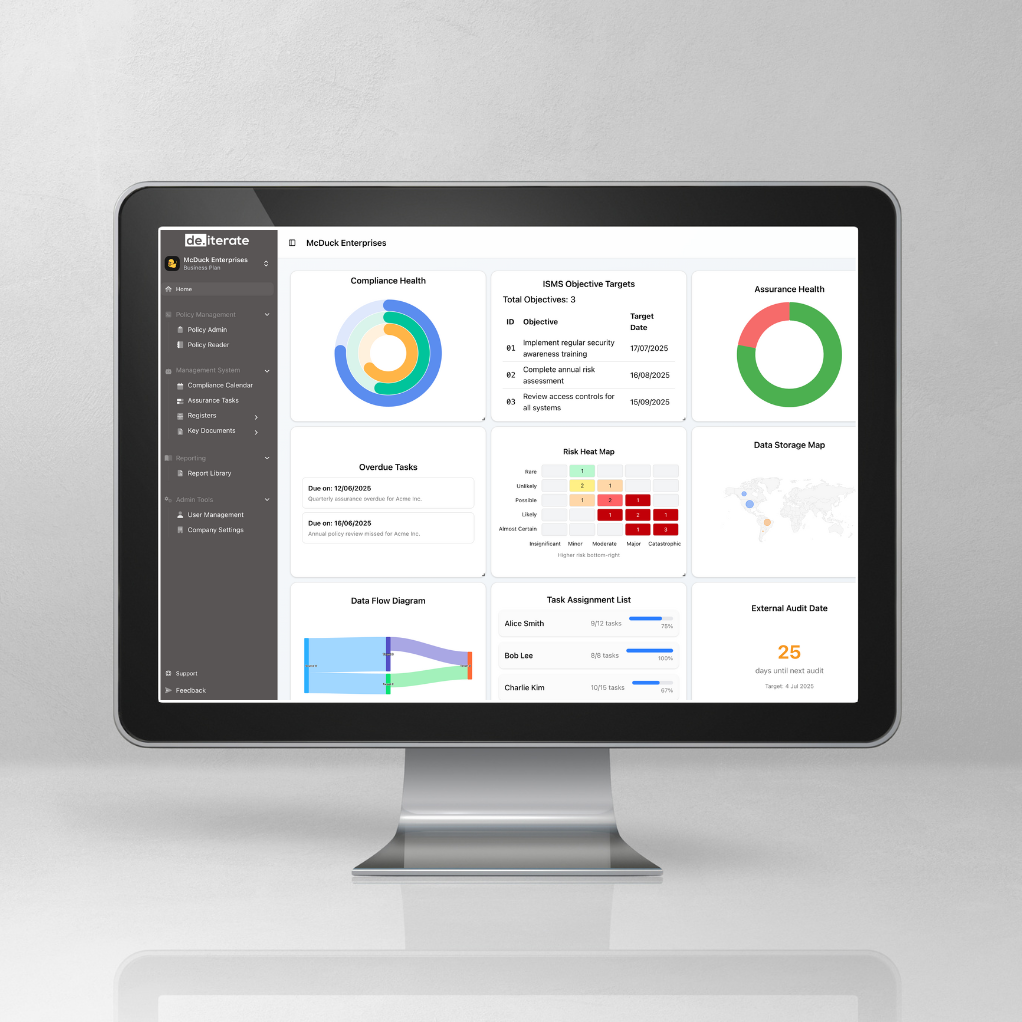
- Start from what you have. Your existing controls, policies and evidence are already in de.iterate, or the Management System Migration Tool can bring them across. Nothing needs rebuilding.
- Map once, use everywhere. Master control mapping connects your controls across the Essential Eight, ISO 27001 and ASD Essentials, so evidence collected once counts wherever it applies.
- Track the gap analysis. Record each action as addressed, partially addressed or not addressed, assign owners to the gaps, and track them through to closure.
- Keep evidence current. Scheduled Assurance Tasks and the Evidence Store make sure your evidence is fresh when your next assessment comes around.
- Keep your obligations straight. Record ASD Essentials and the Essential Eight in your obligations register, so you know which one each customer, contract or regulator expects.
Book a demo and our Aussie GRC experts will walk you through your transition.
Tags: