


Don't just take our word for it
Real stories from teams who’ve achieved and maintained certification, scaled, and succeeded with our platform.
de.iterate is an Australian GRC platform built as one integrated management system (IMS). Every feature in de.iterate runs on the same platform. Risks, controls, obligations, policies, assets, suppliers, audits and evidence all link to each other, so a change in one place shows up everywhere it matters.
de.iterate combines expert-led consulting with an intelligent compliance platform, helping growing organisations embed governance, risk and security into everyday operations. We can help you achieve and maintain certification to ISO 27001, SOC 2, the Privacy Act and a range of other global compliance frameworks, without becoming a compliance expert.
Want to replace spreadsheets, static documents and last-minute audit panic with a smarter, more practical way to manage compliance every day?
Get your ducks in a row with de.iterate.

ISO 27001, Essential Eight, SOC 2, ISO 9001, Privacy Acts and more, all managed in one integrated platform. No duplication. No restarting from scratch.
Move from audit panic to ongoing confidence with compliance embedded everyday. Structured tasks, clear ownership, and year-round assurance.
From start-up to enterprise, de.iterate scales as your organisation grows, without adding complexity or rework.
Saved on compliance
Less compliance costs
To get certified
Most organisations do not have a compliance problem. They have a disconnected-systems problem.
Policies live in one folder. Risks sit in a spreadsheet. Evidence is buried in inboxes and shared drives. Supplier reviews happen somewhere else. Audit prep turns into a last-minute scramble. And somehow, teams are still expected to prove that everything is current, consistent and under control.
de.iterate fixes that.
It brings every moving part of your governance, risk and compliance program into one integrated platform, so your management system is not just documented, it is operational. Policies stay aligned to practice. Risks stay owned. Evidence stays connected to the right controls. Audits become easier. Reporting becomes clearer. And compliance becomes part of how the business runs, not a project everyone dreads.
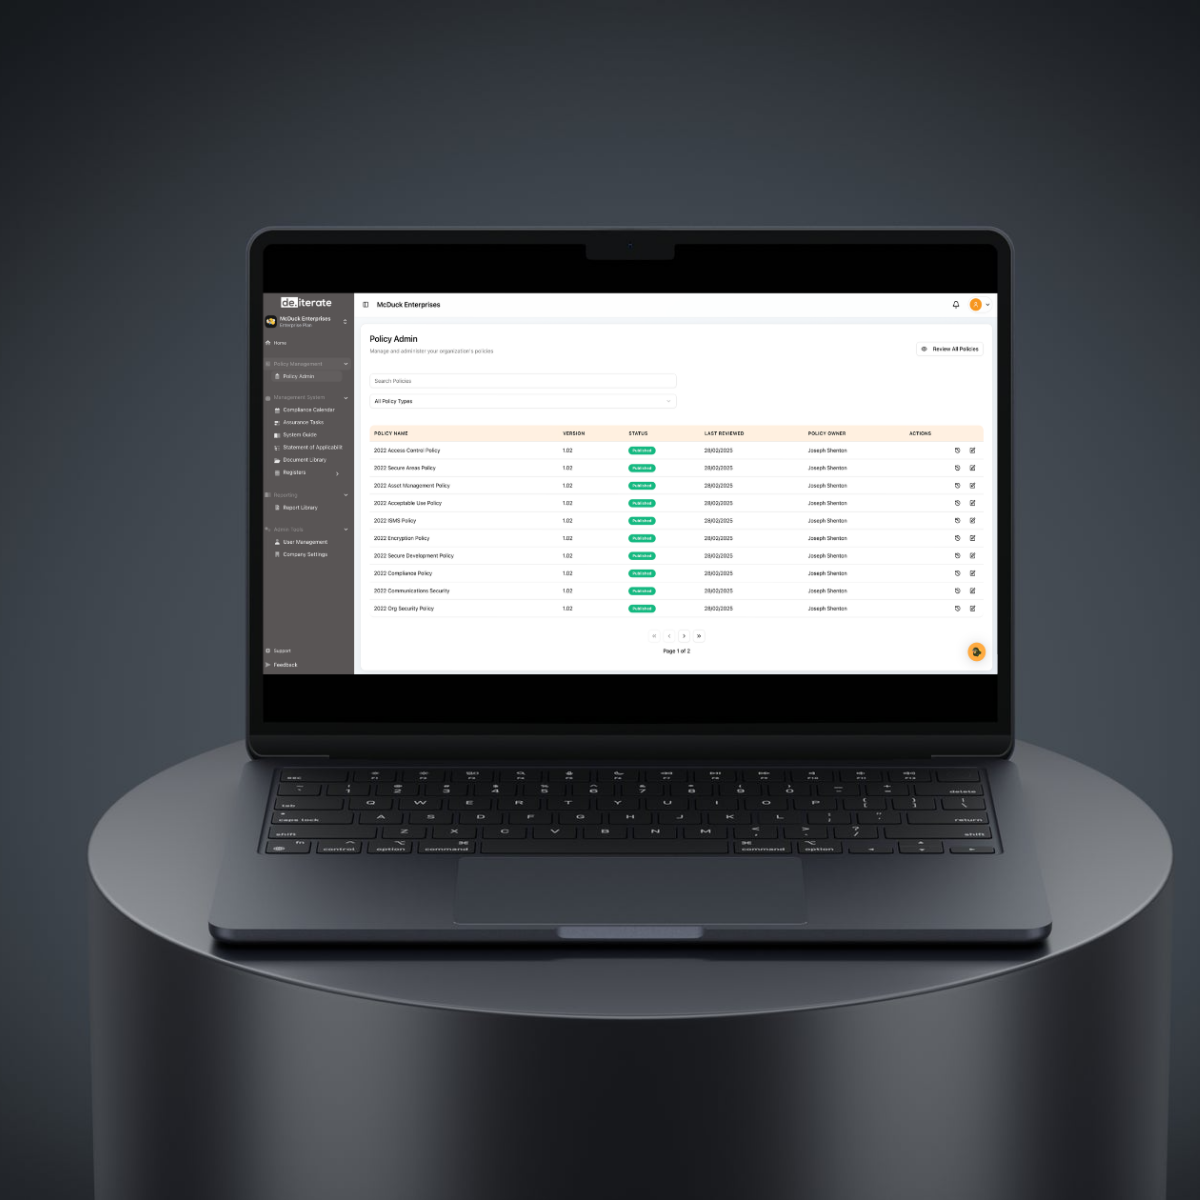

A risk register with a pulse, with inherent and residual scoring, heatmaps and risk appetite.

Every obligation traced to the evidence that meets it, across 25+ frameworks.

Plain-English policies, clear approvals and proof your staff have read them.

Scheduled controls testing, with the evidence ready before your auditor asks.

ISO 42001, AI impact assessments and an inventory of the AI in your business.

Find your personal information, see where it goes and keep your privacy policy current.

ISO 9001, ISO 14001 and ISO 45001, running alongside everything else you manage.

The platform underneath: traceability, integrations, single sign-on and local hosting.
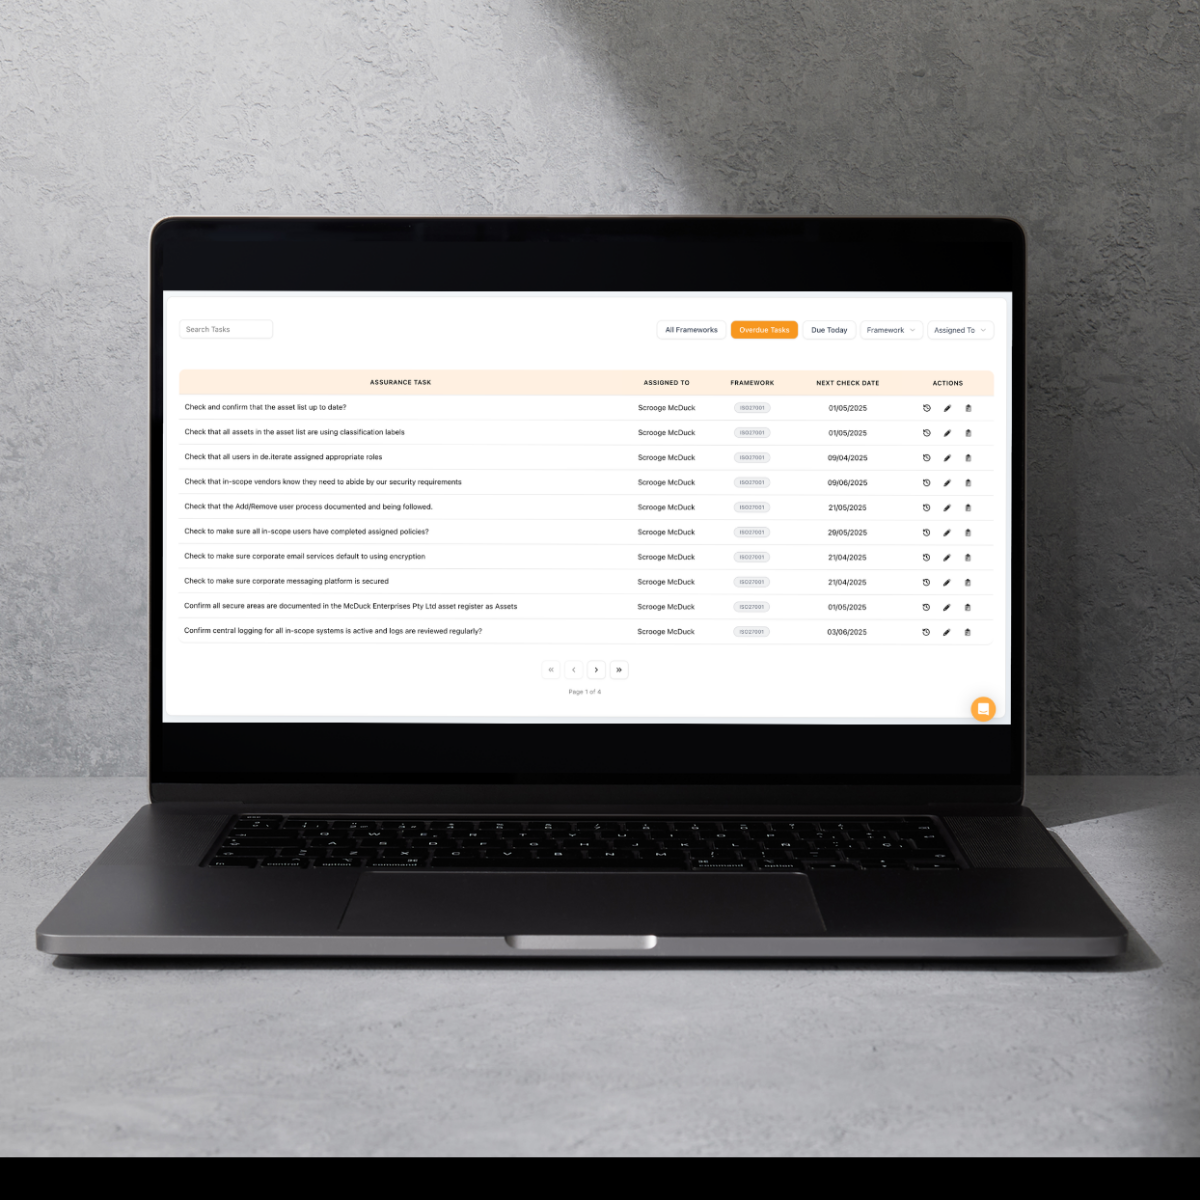
de.iterate is not just software.
We combine technology with hands-on support from experienced GRC professionals based in Australia.
From onboarding through to certification, our team works with you to build momentum quickly, helping many organisations get audit-ready in less than 12 weeks and providing practical support through external audits and ongoing compliance activities.
Our team can even help you migrate your compliance program to de.iterate, without starting from scratch. We help you migrate your existing policies, controls, registers and supporting documentation into one integrated system, so you can preserve the work you’ve already done while moving to a platform built for more practical, continuous compliance.
