The Security Questionnaire Has Quietly Become Part of Your Sales Cycle
The audit is over. The auditor was reasonable. There were four minor nonconformities and a handful of observations, which everyone agrees is a good result.
The team exhales. Someone suggests drinks. The findings report is saved into a folder with a sensible name, and for about eleven weeks nothing whatsoever happens to it.
Then a calendar reminder appears, usually on a Thursday, and it says something like "corrective actions due." And a small, cold feeling enters the room.
The bit nobody prepares for
Enormous amounts of energy go into getting ready for an audit. Almost none goes into what happens afterwards, which is strange, because the afterwards part is where your management system either improves or quietly demonstrates that it can't.
A nonconformity is not a telling-off. It's a finding that something required isn't happening, and the standard expects you to react to it, work out why it occurred, fix it so it doesn't recur, and check that the fix worked. Clause 10.2 in most standards. Short clause, considerable implications.
What usually happens instead is that someone writes a sentence in the findings tracker along the lines of "policy will be updated," marks it closed, and moves on with their life.
Root cause analysis without the theatre
Root cause analysis has a reputation for being a workshop with butcher's paper where everyone agrees the root cause was "lack of resourcing" and then goes back to their desks.
It doesn't need to be that. It needs to answer one question honestly: why did the system allow this to happen?
If the finding is that access reviews weren't completed for two quarters, the cause is rarely that someone was lazy. More often the review was never scheduled, or it was scheduled to a person who changed roles, or it required data that takes four hours to assemble, so it kept losing to more urgent work.
Each of those has a different fix. Only one of them is solved by updating a policy, and it isn't the one most people choose.
Correction and corrective action are different things
Worth being precise about, because auditors are.
The correction is what you do about the immediate problem. Run the overdue access review. Remove the accounts that shouldn't exist.
The corrective action is what you do so it doesn't happen again. Schedule the review as a recurring task with a named owner, a due date and a reminder, and make the data easier to pull so the task takes twenty minutes instead of half a day.
Do only the first and you'll see the same finding next year, at which point it stops being minor.
Give it a name and a date
Findings that belong to everyone belong to nobody. The correction needs a person, not a department, and that person needs to know they've been given it.
The date matters as much as the name. Most certification bodies want corrective action plans within a set window after the audit, often thirty days, with evidence of completion to follow. That timeline arrives faster than anyone expects, particularly across a Christmas break or a financial year end.
Verify, then close
Closing a corrective action because someone said they'd done it is how organisations discover, twelve months later, that they had not.
Verification is small. Look at the evidence. Confirm the recurring task exists and has actually run. Check the register was updated. Write down that you checked, and when, and what you saw.
This is also the part that turns an audit finding into something useful. You end up with a documented history of problems found, causes identified, changes made and results confirmed, which is the clearest possible demonstration that your management system is alive rather than decorative.
The reframe worth having
Findings are free information about where your system doesn't match reality. You paid an expert to come in and look for gaps, and they found some. That's the service working as intended.
The organisations that improve treat the weeks after the audit as the main event. The ones that don't treat the certificate as the finish line and spend the following year slowly recreating the same problems.
Your auditor will be back. They keep the last report.
Need help getting your ducks in a row?
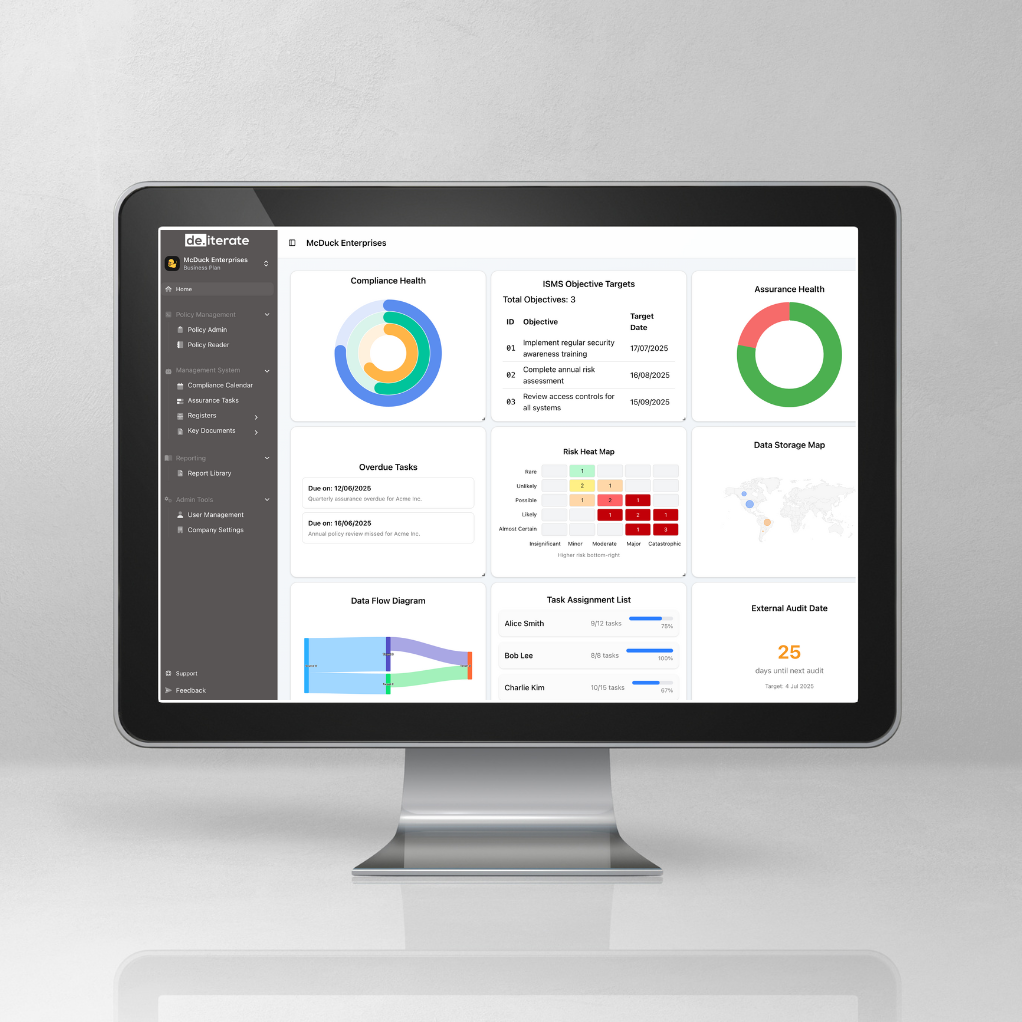
de.iterate tracks findings, corrective actions, owners, due dates and verification evidence in one place, connected to the controls and risks they relate to. So the eleven-week silence after an audit becomes a plan with names on it.
Tags: