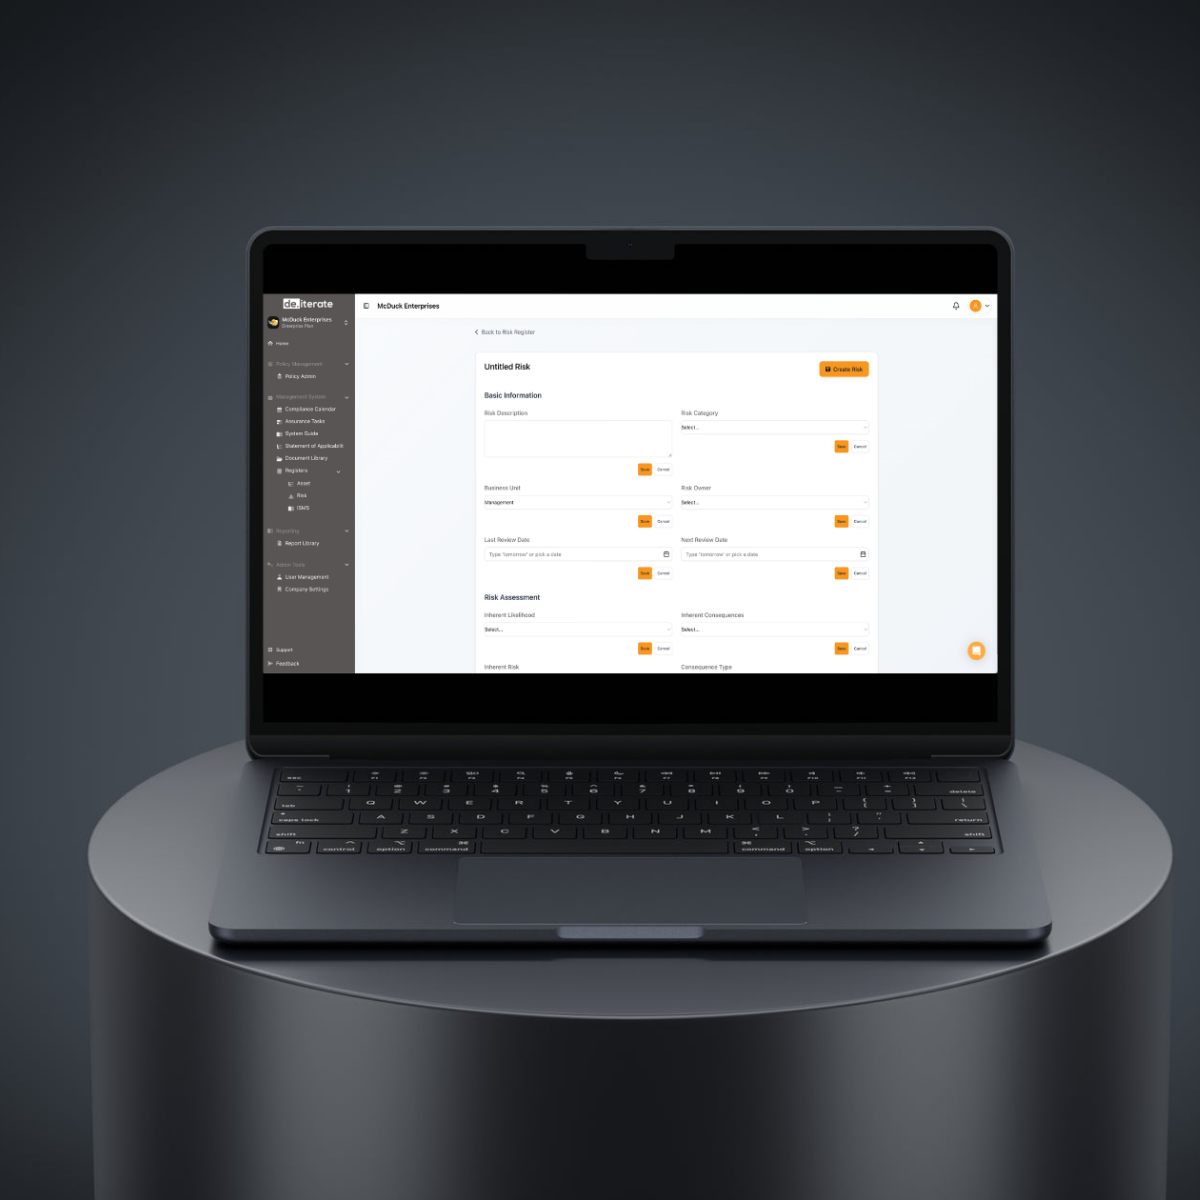
de.iterate is an Australian GRC platform with privacy compliance and data governance built in. You can't protect data you haven't found. de.iterate maps your personal information and data flows, helps you assess privacy risk and keeps your privacy obligations up to date. Your privacy policy even updates itself.
Instead of managing policies in one place, risks in another, evidence in folders, and audits through a last-minute scramble, de.iterate connects the whole system. That means better visibility, clearer ownership, stronger assurance and less time lost to manual admin. The current platform spans policies, assurance tasks, registers, evidence, reporting, Trust Centre capabilities, auditor access and support for multiple frameworks.
We help you get your ducks in a row.
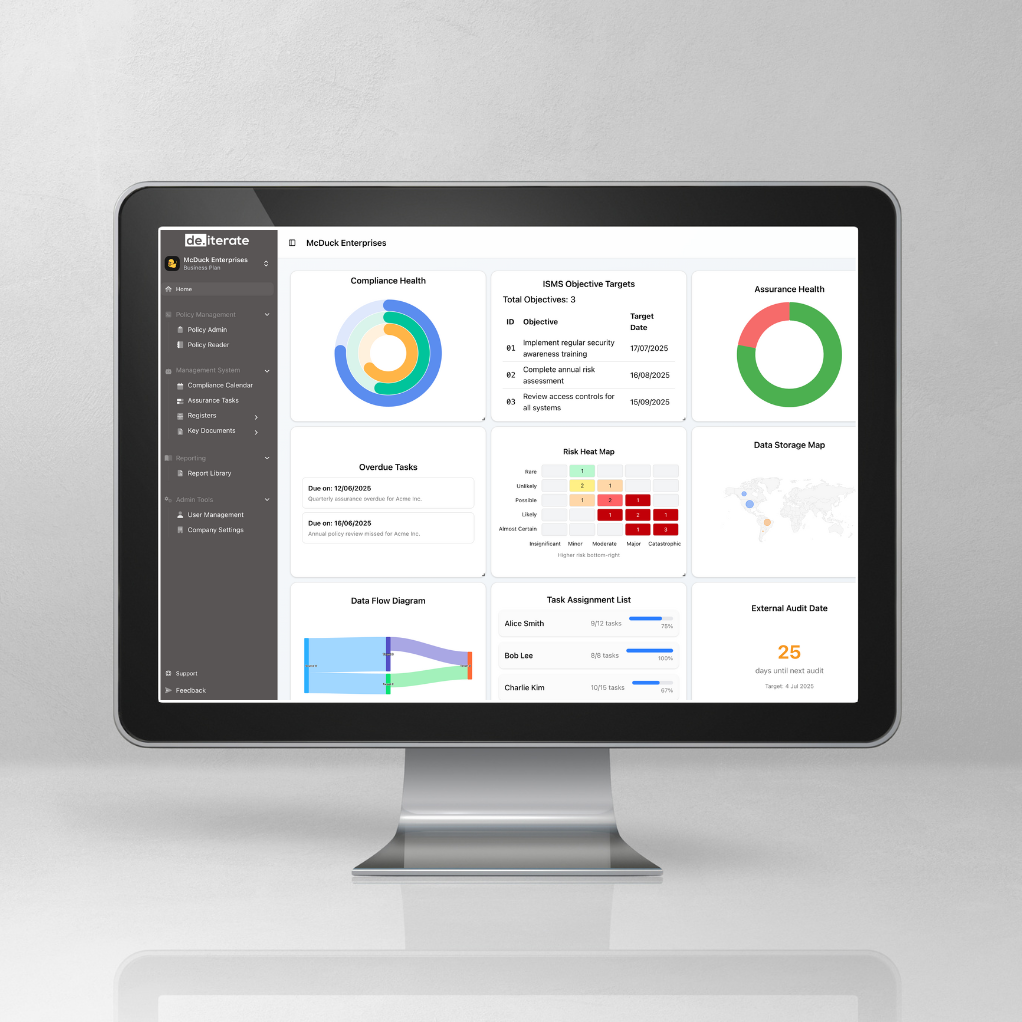
The statutory tort for serious invasions of privacy has been in force since June 2025. From 10 December 2026, privacy policies must explain when computers make, or substantially contribute to, decisions that significantly affect people. Meanwhile, your privacy policy was last reviewed by a lawyer in 2021, and your data map is a photo of a whiteboard on someone’s phone.
Larger organisations have a privacy office, a data map in a platform and a policy reviewed every year. The data map was built for the 2018 GDPR project and describes the systems the organisation had then. Since then, the business has added a hundred SaaS tools, three of which make decisions about customers, and the privacy team learned about two of them from this page. The December deadline asks a specific question: which of your systems make or substantially contribute to decisions that significantly affect people? The privacy team can answer for the systems it knows about. Credit, fraud, recruitment screening and the vendor features switched on last quarter sit with four other teams, none of whom have been asked.
AI governance works when you know which AI systems you have, including the ones your vendors switched on, someone is accountable for each, and the controls around them grow out of the security and privacy work you’ve already done rather than starting a third program from scratch. de.iterate is built that way. AI systems sit in de.iterate's register that links to your suppliers and risks, impact assessments and approvals are recorded against each one, and the AI management system shares its controls and testing with ISO 27001 and privacy, so “who is responsible for AI?” has an answer with a name on it.
Build your AI management system with ISO foundations and map it to international standards and obligations. AI control design and testing are shared with your existing ISO 27001 and privacy programs, so your AI risk management naturally develops out of the foundations you already have.
Record your AI systems in de.iterate's configurable register, with the fields your AI management system needs. AI tools that touch your data cross-link with your de.iterate supplier registers, where you can note where the data goes and link each tool to your AI risks and controls.
Every automated suggestion in de.iterate arrives as a draft, with its reasoning and confidence stored alongside it. A human approves it before anything changes, which is the same kind of oversight management asks of you.
Each entry in the AI register carries an accountable owner, a business purpose and a review date, with roles mapped to the responsibilities ISO 42001 expects. When an auditor asks who is responsible for AI, the answer is a list of named people rather than a committee.
Start from an AI acceptable use policy written by de.iterate's GRC experts. Distribute it through de.iterate's policy module, track who has read it, and reset attestation when the rules change, so the developer pasting code into a chatbot has seen the policy that says not to.
Assess the impact of each AI system on people and on your organisation, and keep a record of the risks, decisions, controls and approvals that follow, as well as the evidence that each step took place.
Most questions about privacy come down to jurisdiction: which laws de.iterate covers, where your data is stored, and what the Australian reforms will require of you by December. The answers below cover the detail, and our GRC team can work through the reforms with you if your situation isn’t straightforward.
Yes. The Privacy Act framework is built into de.iterate, and our Aussie GRC experts can help you work through what the reforms mean for your business. Configurable reform obligations are on the roadmap.
With de.iterate, you choose Australia or the EU. Production data, backups and disaster recovery all stay in that jurisdiction.
A privacy impact assessment (PIA) looks at how a project, system or process will handle personal information, and identifies privacy risks before they cause harm. It's a common expectation under the Privacy Act and GDPR for anything new that uses personal information.
Yes. GDPR and ISO 27701 are built into de.iterate, along with the Privacy Acts for Australia, New Zealand, Canada, France, Italy, the US and the UK.
Yes. In de.iterate, requests from individuals about their personal information go through a tracked workflow, so each one gets a timely response and a record.
You embed de.iterate's dynamic privacy policy on your website with a short piece of code, alongside your collection notice. When your privacy program changes in de.iterate, both update automatically.
The statutory tort for serious invasions of privacy has applied since June 2025. From 10 December 2026, privacy policies must disclose when computers make, or substantially contribute to, decisions that significantly affect people. Our Aussie GRC experts can help you work out what this means for your business.
From setup to scale, every feature is designed to help your team save time, stay focused, and drive meaningful results.
de.iterate combines technology with hands-on support from experienced GRC professionals based in Australia. From onboarding through to certification, our team works with you to build momentum quickly, helping many organisations get audit-ready in less than 12 weeks and providing practical support through external audits and ongoing compliance activities.
Great compliance is not built in the two weeks before an audit. de.iterate helps you stay ready year-round with assurance tasks, checklists, live registers, reporting and a compliance calendar that keeps momentum going.
From start-ups to enterprise, de.iterate supports multiple frameworks in one system, including ISO 27001, ISO 27701, ISO 9001, ISO 14001, ISO 45001, Privacy Acts, SOC 2, DIP, Essential Eight and more. You can grow your compliance maturity without rebuilding everything from scratch.
Many tools stop at storage. de.iterate goes further by connecting your policies, controls, evidence, registers and assurance activity in context. That means your documentation is not just centralised, it is structured, linked and easier to defend.
We believe compliance should be simpler, clearer and more achievable. That is why de.iterate combines structured workflows, smart documentation, migration support and guided onboarding with a platform that is intuitive enough for teams to use every day.
de.iterate is designed for the way organisations actually work. Policies, risks, assets, incidents, suppliers, evidence, audits and reporting all sit in one integrated platform, so compliance becomes part of business as usual.
A risk register with a pulse, with inherent and residual scoring, heatmaps and risk appetite.
Every obligation traced to the evidence that meets it, across 25+ frameworks.
Plain-English policies, clear approvals and proof your staff have read them.
Scheduled controls testing, with the evidence ready before your auditor asks.
ISO 42001, AI impact assessments and an inventory of the AI in your business.
ISO 9001, ISO 14001 and ISO 45001, running alongside everything else you manage.
With de.iterate, the complexity of managing multiple frameworks doesn’t translate into increased workload. Our unified platform serves as a central hub for overseeing all your compliance activities, whether you’re working with bespoke frameworks or seeking to meet the criteria of the most sought-after security and privacy standards and certifications.
The global standard for building EMS. It gives you a structure to identify environmental impacts, manage obligations, strengthen governance.
This standard specifies the requirements for managing AI systems responsibly and ethically. It helps ensure trustworthy development and use of AI.
This specifies how organisations should manage their customer’s data. It is one of the most sought-after security framework for SaaS companies.
Country-specific legislative frameworks established to protect individuals’ personal information from misuse, interference, unauthorised access, modification, and disclosure.
The Australian Government’s Department of Employment and Workplace Relations uses the External Systems Accreditation Framework and the RFFR approach to assess and accredit third party service providers and systems.
DISP is a critical initiative that ensures businesses in the defence supply chain meet stringent security requirements. DISP compliance is essential for companies that engage in Defence tenders, contracts and projects.
de.iterate pricing is structured around the compliance frameworks you choose to access, giving you the flexibility to build a program that fits your organisation’s needs. Every plan includes access to the de.iterate platform and its feature set, from automated and expert-led onboarding, through to migration support, assurance workflows, live registers, compliance reporting and the core documentation needed to run and maintain your management system with confidence.
Essential Eight
SMB 1001
Privacy Acts
DISP
Cyber Essentials
ISO 27001
ISO 27701
ISO 42001
ISO 9001
ISO 45001
ISO 14001
SOC 2
NIST CSF 2.0
NIST 800-53
NIST 800-172
NIST 800-172
GDPR
Essential Eight
SMB 1001
Privacy Acts
DISP
Cyber Essentials
DORA
NIS2
CIS v8
EU AI Act
TISAX
ISO 27001
ISO 27701
ISO 42001
ISO 9001
ISO 45001
ISO 14001
SOC 2
NIST CSF 2.0
NIST 800-53
NIST 800-171
NIST 800-172
GDPR
Essential Eight
SMB 1001
Privacy Acts
DISP
ISM
SOCI
Right Fit for Risk (RFFR)
Cyber Essentials
DORA
NIS2
CIS c8
EU AI Act
TISAX
We'll show you your data flows, register and privacy policy working together in a live demo.