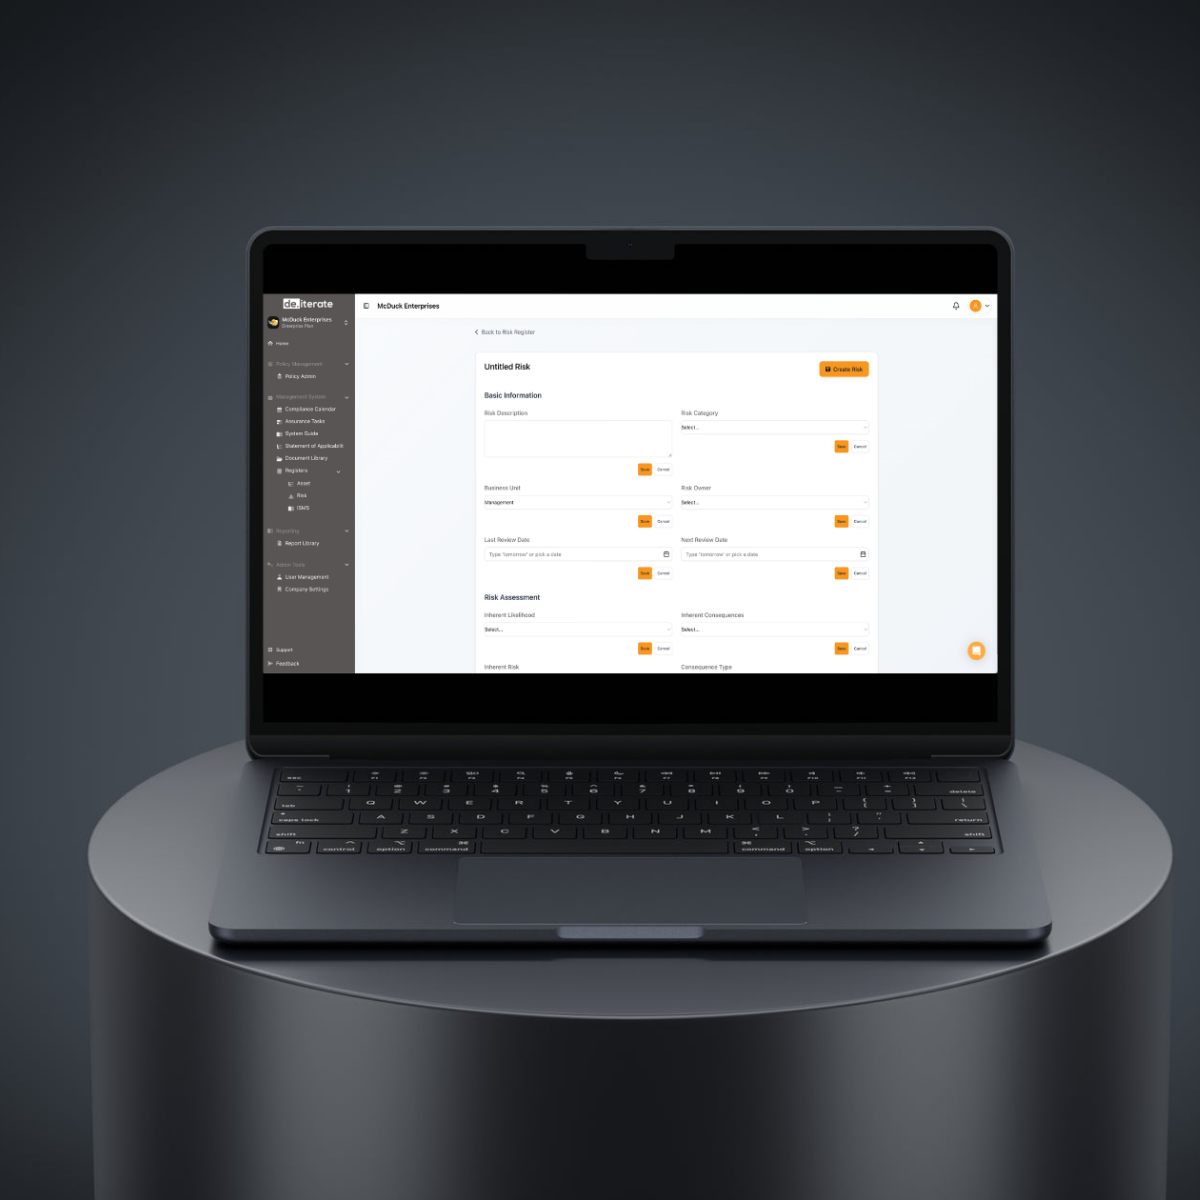
de.iterate is an Australian GRC platform built as one integrated management system (IMS). Every feature in de.iterate runs on the same platform. Risks, controls, obligations, policies, assets, suppliers, audits and evidence all link to each other, so a change in one place shows up everywhere it matters.
Instead of managing policies in one place, risks in another, evidence in folders, and audits through a last-minute scramble, de.iterate connects the whole system. That means better visibility, clearer ownership, stronger assurance and less time lost to manual admin. The current platform spans policies, assurance tasks, registers, evidence, reporting, Trust Centre capabilities, auditor access and support for multiple frameworks.
We help you get your ducks in a row.
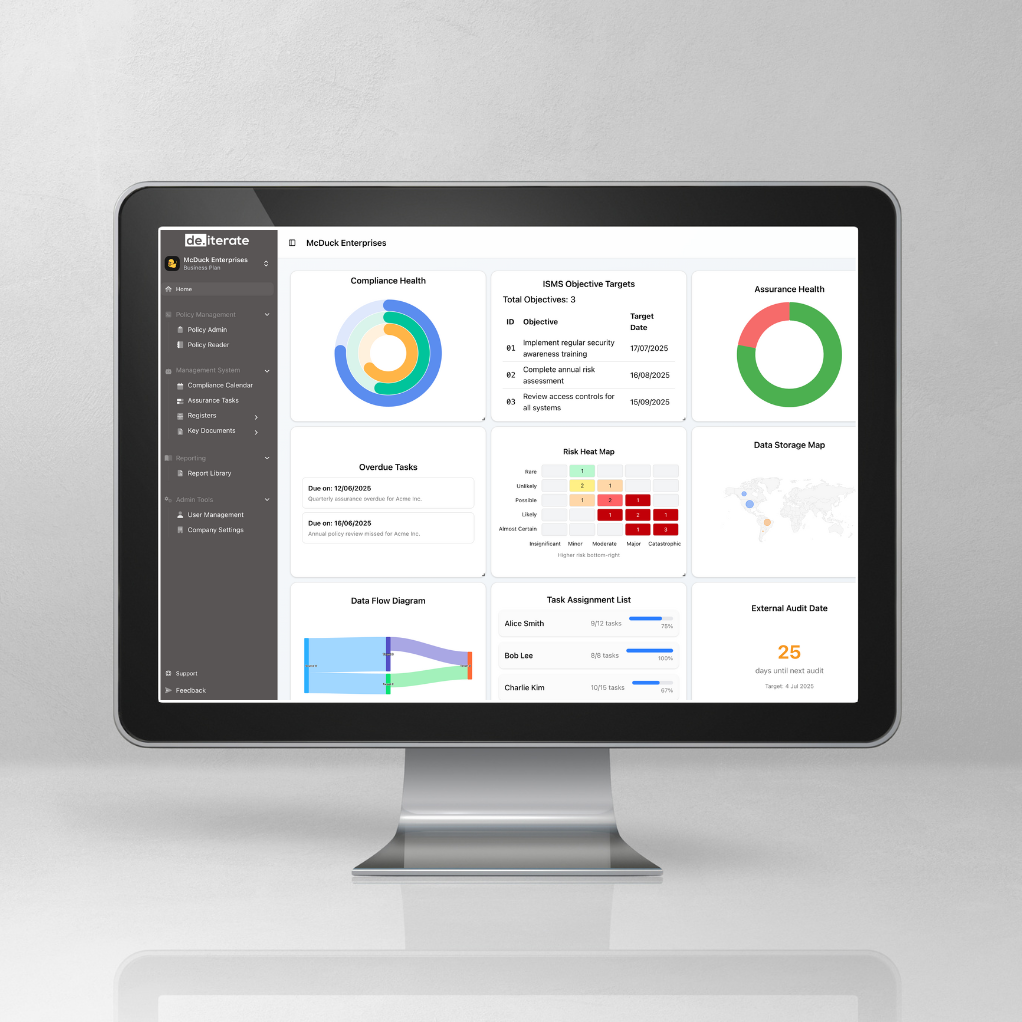
Policies sit in one folder, risks in a spreadsheet, evidence in inboxes and supplier reviews somewhere else again. Each piece works fine on its own. The trouble starts when someone asks how they fit together.
Larger organisations have a platform for each piece. Policies live in the document system, risks in the GRC tool, vendors in the procurement platform, incidents in the service desk, and evidence in a shared drive organised by audit year. Each has an owner, a licence and its own idea of what a control is called. The connections between them exist in a quarterly reconciliation run by one analyst, who knows that “AC-02” in one tool is “Access Control 2.1” in another and “User access management” in a third. The auditor asks how the supplier breach in March relates to the risk rated low in February and the control tested in January, and the answer takes a week.
That gap is now supercharged by auditors who are using AI, who can cross-check every register against every other one in minutes, and will.
Each part of a management system is manageable on its own. The work is in the joins: which control meets which obligation, which supplier touches which data, which incident changes which risk. de.iterate’s fabric holds those joins so nobody has to, and the rest of the platform is built to keep them intact, with your data where you choose, your tools connected, your people told what’s theirs, and every link visible in either direction when the auditor asks.
The de.iterate fabric connects every part of your management system. Start from an obligation and follow it to its policy, control, risk, asset and evidence, or start from any of those and work back. Visualise the connections using the platforms inbuilt fabric explorer.
Connect de.iterate to your technology ecosystem using our inbuilt integrations, or bring your own using public API, with granular role-based access control you can connect your own systems safely.
Plan and run every audit for multiple standards concurrently in de.iterate's Audit Centre. Record nonconformities, assign corrective actions to owners and track each one through to closure.
Roles and permissions cover company admins, policy readers and duties such as asset owner. Notifications and the Compliance Calendar tell each person what's theirs and when it's due, and custom dashboards with heatmaps keep boards and managers in the picture.
Give each site its own incident log, corrective actions and local records inside de.iterate's group management system. Site coordinators work in their own view, and head office sees every site without asking anyone to send a spreadsheet.
de.iterate's dashboards pull open nonconformities, incident trends, overdue actions and audit status across every standard and site. The management review runs from live data, and minutes and decisions recorded for the next audit.
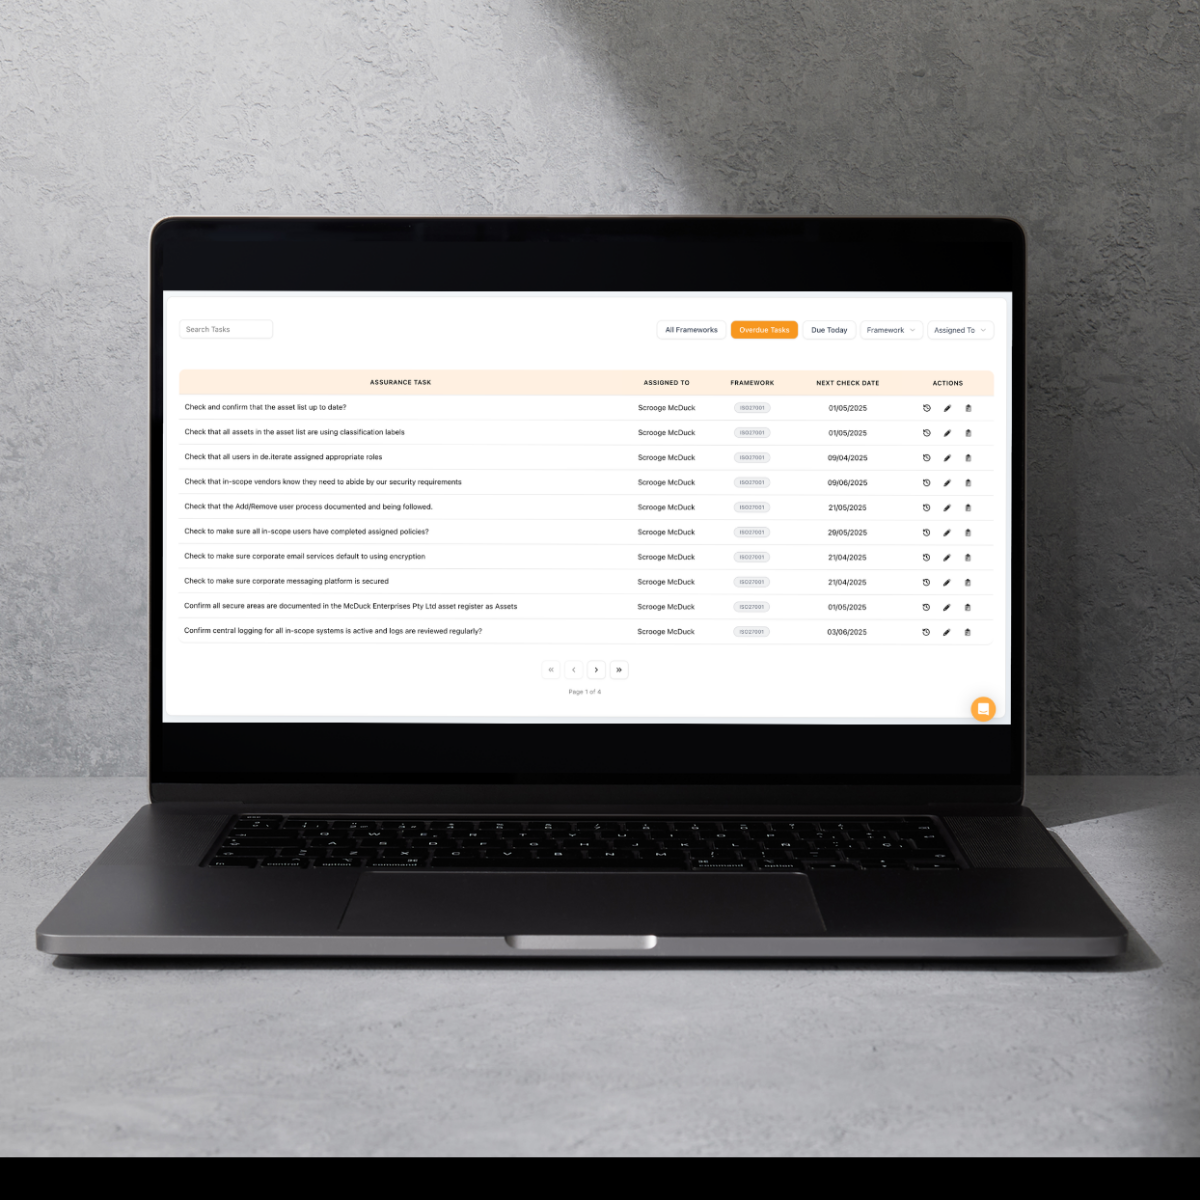
Most questions about the platform itself come down to trust and fit: where your data lives, how de.iterate connects to what you already run, and what happens when you need help. The answers below cover the detail, from hosting to sign-on to the people on the other end of the chat.
With de.iterate, you choose Australia or the EU. Production, backups and disaster recovery all stay in your chosen jurisdiction.
Yes. de.iterate's SharePoint and Confluence integrations are live, our public API is available now, and more connectors are on the way. If there's one you'd like us to prioritise, reach out and [book a demo] and we’ll show you how it would look in the platform.
Yes. de.iterate's multi-tenancy view is built for MSPs and advisers who manage more than one organisation. Interested in reselling de.iterate? Take a look at our Partner Program.
Yes. Staff can sign in to de.iterate with SAML or OpenID Connect, and users sync from Microsoft Entra ID. You can also let colleagues auto-join using authorised email domains.
Yes. de.iterate's dedicated development, test, UAT and production environments mean changes are tested before they reach your live system.
Through the de.iterate Trust Centre, either as a public web page or a secure private link.
Harold, our in-platform assistant, offers guidance inside de.iterate. You can also search the knowledge base or chat with our Aussie GRC experts in the app.
From setup to scale, every feature is designed to help your team save time, stay focused, and drive meaningful results.
de.iterate combines technology with hands-on support from experienced GRC professionals based in Australia. From onboarding through to certification, our team works with you to build momentum quickly, helping many organisations get audit-ready in less than 12 weeks and providing practical support through external audits and ongoing compliance activities.
Great compliance is not built in the two weeks before an audit. de.iterate helps you stay ready year-round with assurance tasks, checklists, live registers, reporting and a compliance calendar that keeps momentum going.
From start-ups to enterprise, de.iterate supports multiple frameworks in one system, including ISO 27001, ISO 27701, ISO 9001, ISO 14001, ISO 45001, Privacy Acts, SOC 2, DIP, Essential Eight and more. You can grow your compliance maturity without rebuilding everything from scratch.
Many tools stop at storage. de.iterate goes further by connecting your policies, controls, evidence, registers and assurance activity in context. That means your documentation is not just centralised, it is structured, linked and easier to defend.
We believe compliance should be simpler, clearer and more achievable. That is why de.iterate combines structured workflows, smart documentation, migration support and guided onboarding with a platform that is intuitive enough for teams to use every day.
de.iterate is designed for the way organisations actually work. Policies, risks, assets, incidents, suppliers, evidence, audits and reporting all sit in one integrated platform, so compliance becomes part of business as usual.
A risk register with a pulse, with inherent and residual scoring, heatmaps and risk appetite.
Every obligation traced to the evidence that meets it, across 25+ frameworks.
Plain-English policies, clear approvals and proof your staff have read them.
Scheduled controls testing, with the evidence ready before your auditor asks.
ISO 42001, AI impact assessments and an inventory of the AI in your business.
Find your personal information, see where it goes and keep your privacy policy current.
With de.iterate, the complexity of managing multiple frameworks doesn’t translate into increased workload. Our unified platform serves as a central hub for overseeing all your compliance activities, whether you’re working with bespoke frameworks or seeking to meet the criteria of the most sought-after security and privacy standards and certifications.
The global standard for building EMS. It gives you a structure to identify environmental impacts, manage obligations, strengthen governance.
This standard specifies the requirements for managing AI systems responsibly and ethically. It helps ensure trustworthy development and use of AI.
This specifies how organisations should manage their customer’s data. It is one of the most sought-after security framework for SaaS companies.
Country-specific legislative frameworks established to protect individuals’ personal information from misuse, interference, unauthorised access, modification, and disclosure.
The Australian Government’s Department of Employment and Workplace Relations uses the External Systems Accreditation Framework and the RFFR approach to assess and accredit third party service providers and systems.
DISP is a critical initiative that ensures businesses in the defence supply chain meet stringent security requirements. DISP compliance is essential for companies that engage in Defence tenders, contracts and projects.
de.iterate pricing is structured around the compliance frameworks you choose to access, giving you the flexibility to build a program that fits your organisation’s needs. Every plan includes access to the de.iterate platform and its feature set, from automated and expert-led onboarding, through to migration support, assurance workflows, live registers, compliance reporting and the core documentation needed to run and maintain your management system with confidence.
Essential Eight
SMB 1001
Privacy Acts
DISP
Cyber Essentials
ISO 27001
ISO 27701
ISO 42001
ISO 9001
ISO 45001
ISO 14001
SOC 2
NIST CSF 2.0
NIST 800-53
NIST 800-172
NIST 800-172
GDPR
Essential Eight
SMB 1001
Privacy Acts
DISP
Cyber Essentials
DORA
NIS2
CIS v8
EU AI Act
TISAX
ISO 27001
ISO 27701
ISO 42001
ISO 9001
ISO 45001
ISO 14001
SOC 2
NIST CSF 2.0
NIST 800-53
NIST 800-171
NIST 800-172
GDPR
Essential Eight
SMB 1001
Privacy Acts
DISP
ISM
SOCI
Right Fit for Risk (RFFR)
Cyber Essentials
DORA
NIS2
CIS c8
EU AI Act
TISAX
We'll show you how it all connects, starting with the part that matters most to you.