Your whole GRC program, connected in one platform

Everything connected, so you only do the work once.

Risk, compliance, policy, audit and assurance in one integrated management system, with Aussie GRC experts to help you get your ducks in a row.

de.iterate is an Australian GRC platform built as one integrated management system (IMS). Every feature in de.iterate runs on the same platform. Risks, controls, obligations, policies, assets, suppliers, audits and evidence all link to each other, so a change in one place shows up everywhere it matters.

Instead of managing policies in one place, risks in another, evidence in folders, and audits through a last-minute scramble, de.iterate connects the whole system. That means better visibility, clearer ownership, stronger assurance and less time lost to manual admin. The current platform spans policies, assurance tasks, registers, evidence, reporting, Trust Centre capabilities, auditor access and support for multiple frameworks.

Pick a capability below to see how it works, or book a demo and we'll walk you through the parts that matter most to you.
deiterate-platform
hours-saved

100s of hours

Saved on compliance

reduce-cost

54%

Lower compliance costs

faster-compliance

12 weeks

To get certified

risk-register-mock-up

Start where you are

Not sure where to begin? Pick the description that sounds most like you.

Explore de.iterate by capability

A smarter way to manage compliance

de.iterate combines policies, training, registers, evidence, reporting and assurance workflows in one integrated management system, helping you reduce complexity, stay audit-ready and turn governance, risk management and compliance into business as usual. Every feature is designed to save time, strengthen accountability and make GRC compliance easier to manage across your organisation.
compliance-management

Enterprise Risk Management

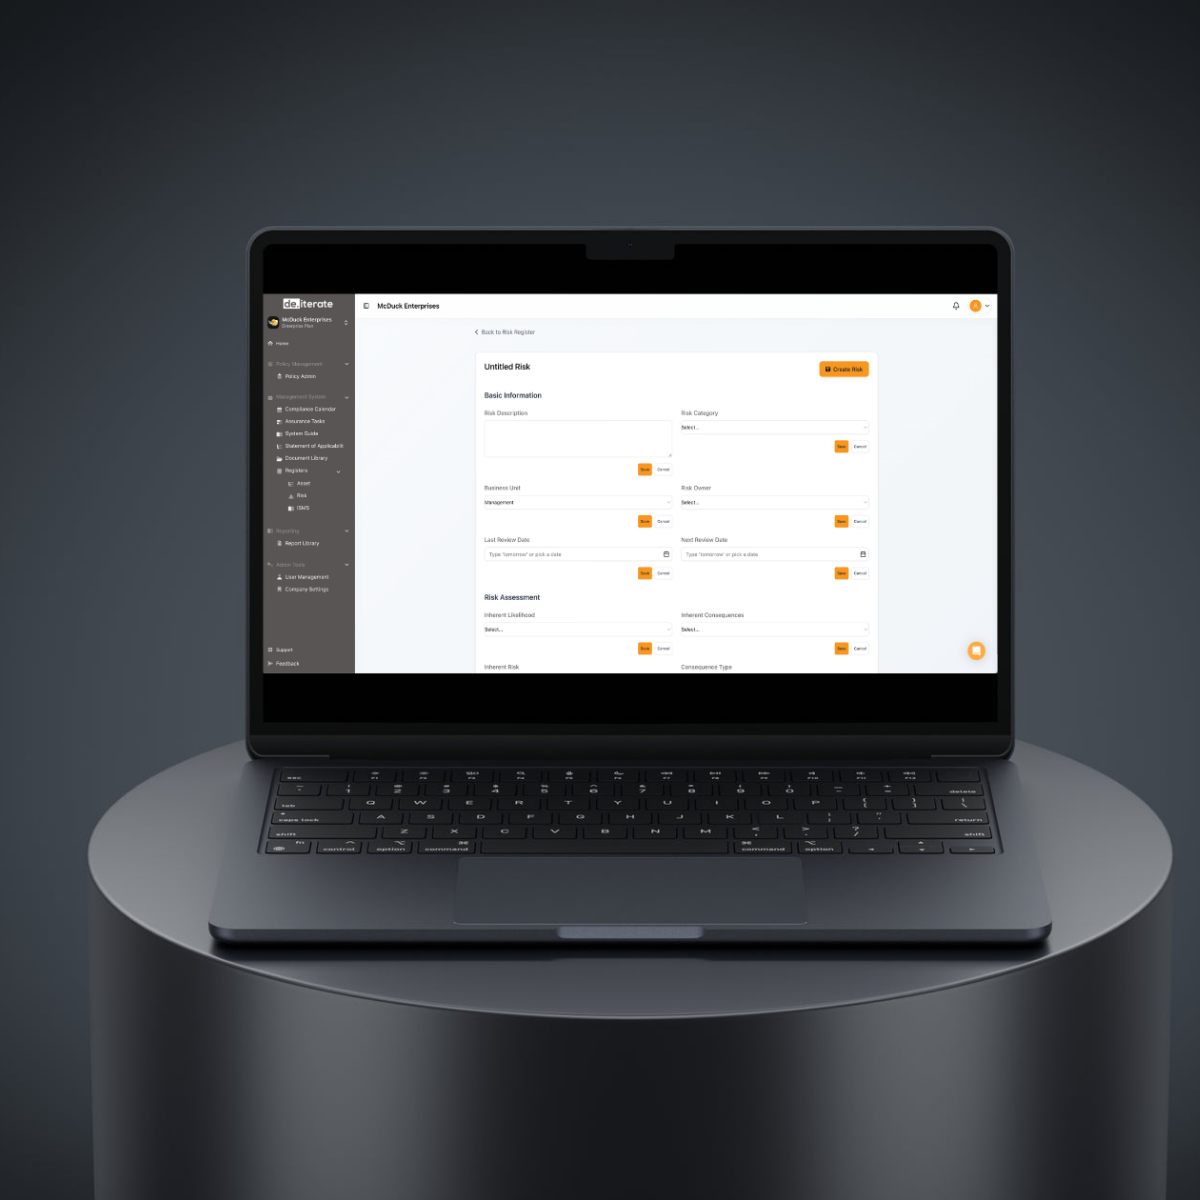
 A risk register with a pulse, with inherent and residual scoring, heatmaps and risk appetite. 

board-reporting

Compliance Management

 Every obligation traced to the evidence that meets it, across 25+ frameworks.

policy-management

Policy Management

 Plain-English policies, clear approvals and proof your staff have read them. 

controls-management

Controls Management

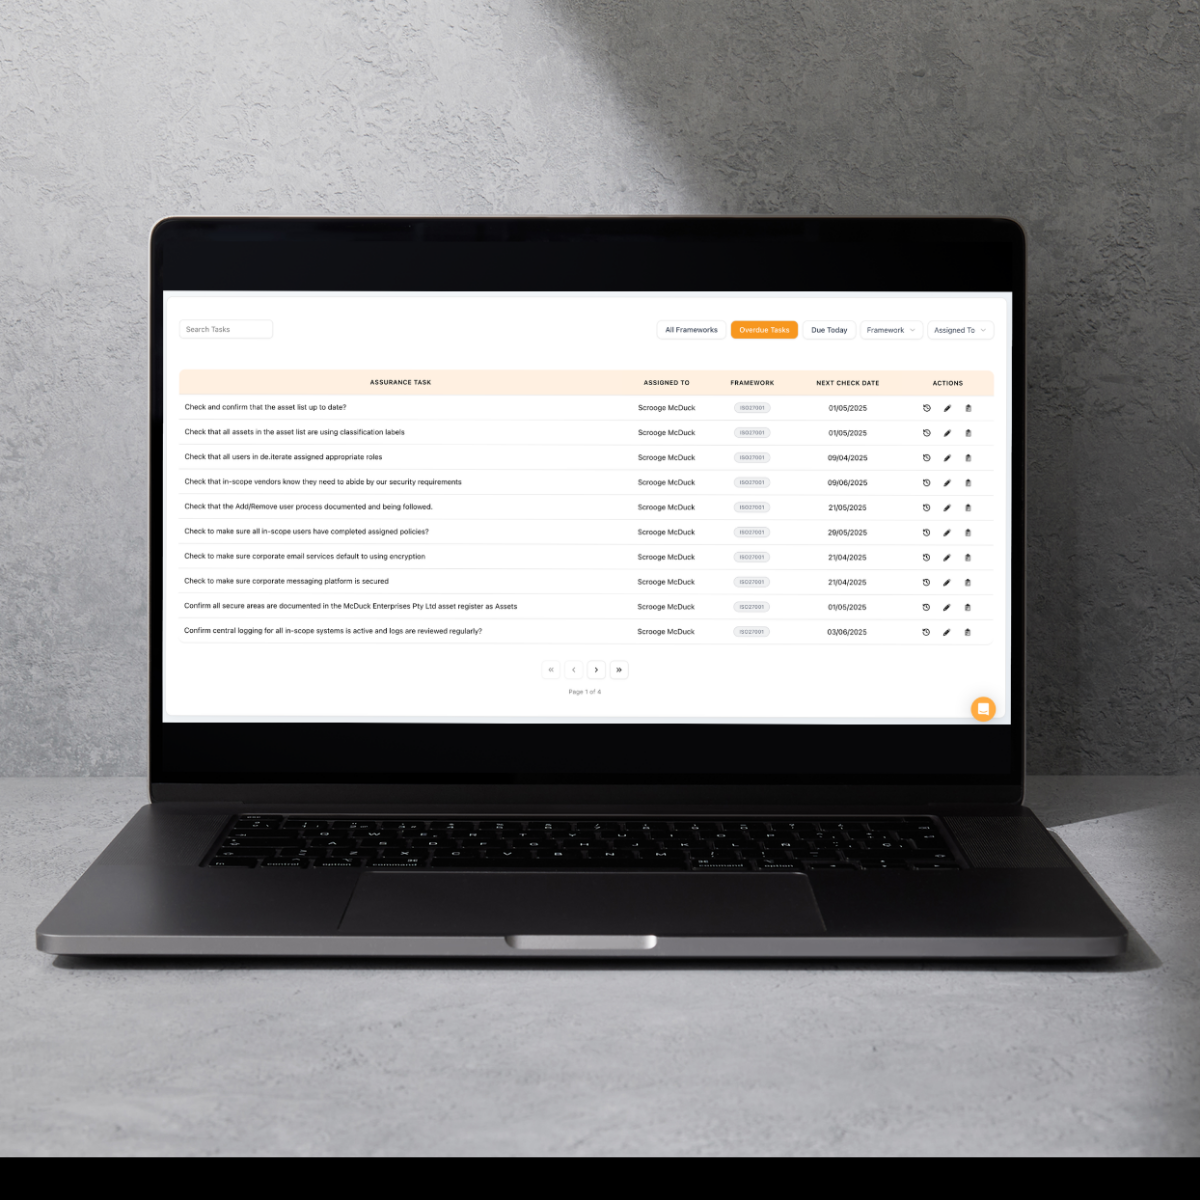
 Scheduled controls testing, with the evidence ready before your auditor asks. 

supplier

Third Party Risk Management

Keep tabs on the suppliers holding a slice of your risk.

it-cyber-security-consultants

Cyber & IT Risk

 Your whole ISMS, from asset register to Statement of Applicability.

AI-gov

AI Governance

 ISO 42001, AI impact assessments and an inventory of the AI in your business. 

data-privacy

Privacy & Data Governance

 Find your personal information, see where it goes and keep your privacy policy current.

audit-management

Audit Management

 Audit programs, findings and corrective actions tracked to closure. 

quality-safety-enviro

Quality, Safety and Environment

 ISO 9001, ISO 14001 and ISO 45001, running alongside everything else you manage. 

deiterate-integrations

Integrated Management System

 The platform underneath: traceability, integrations, single sign-on and local hosting. 
assurance-task-mock-up

What's new in de.iterate

We've been busy. Here's what's landed recently, and what's coming next.

  • Integrations: SharePoint and Confluence are live, with more on the way.
  • Public API: connect your own systems with granular role-based access control.
  • Audit Centre: audit programs, findings and corrective actions in linked registers.
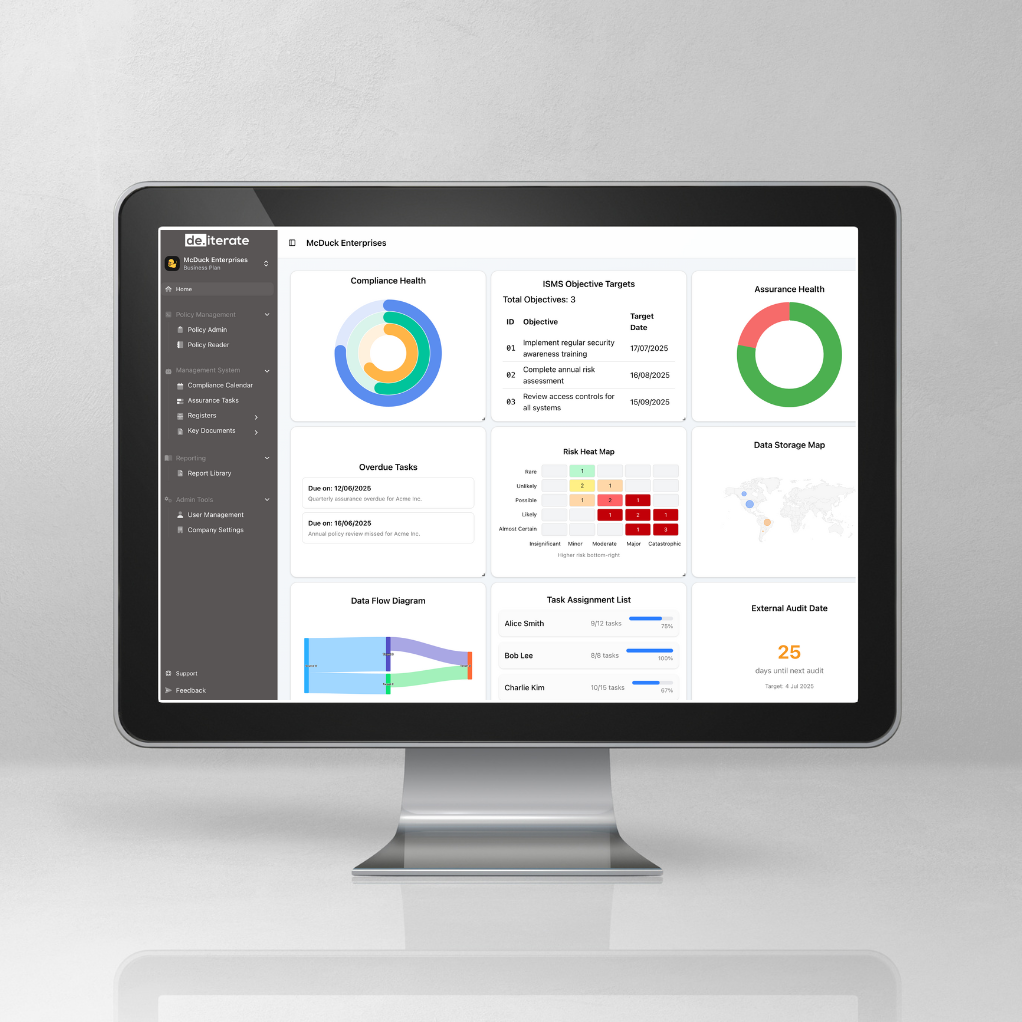
  • Risk heatmaps and risk appetite: see your risk at a glance and know when it moves outside tolerance.
  • AI impact assessments: assess each AI system, with a record of decisions and approvals.
  • Hosting in Australia or the EU: production, backups and disaster recovery in your chosen jurisdiction.
  • Key Risk Indicators: live metrics attached to your risks, connected to your integrations.

What makes de.iterate different

Most GRC platforms are built for the compliance team and bought by the compliance team, which is why the rest of the business sends its updates by email. de.iterate is built so the work is done once, checked by a person, understood by the people who own the risks and controls, and supported by experts who answer the phone. The difference shows up in how quickly you’re audit-ready and in how little of the program depends on one person.

follow-thread

Follow the thread in any direction

The de.iterate fabric connects every part of your management system. Start from an obligation and follow it to its policy, control, risk, asset and evidence, or start from any of those and work back. Visualise the connections using the platforms inbuilt fabric explorer.

de.iterate-APIs

Plug into the tools you already use

Connect de.iterate to your technology ecosystem using our inbuilt integrations, or bring your own using public API, with granular role-based access control you can connect your own systems safely.

plan-annual-audit

One audit program for every standard

Plan and run every audit for multiple standards concurrently in de.iterate's Audit Centre. Record nonconformities, assign corrective actions to owners and track each one through to closure.

aussie-experts

Real GRC experts, based in Australia

Our Aussie GRC experts help from onboarding through to certification and beyond. Many organisations are audit-ready in under 12 weeks.

ai-rules

AI you can validate

Every AI suggestion arrives as a draft, with its reasoning and confidence on show. You decide whether it goes in. We're certified to ISO 42001 ourselves, so we hold our own AI to the standard we help you meet.

reporting

Reporting made easy

de.iterate's dashboards pull open nonconformities, incident trends, overdue actions and audit status across every standard and site. The management review runs from live data, and minutes and decisions recorded for the next audit.

know-who-signed-off

Room to grow

Start with your first self-assessment, move onto certification and then keep going all the way to enterprise and government tenders, without rebuilding anything along the way. On integrated system, without the duplication.

auditor-portal-1

Auditors get a login, not a folder

de.iterate's Auditor Portal lets your external auditor review documents, controls and evidence directly, or you can hand over an export pack. Fewer email chains, a calmer audit week, and evidence that’s already where the auditor expects to find it.

policy-worth-reading

No need to be a compliance expert

Risk owners, policy readers and asset owners work in plain screens with your scales already applied, and the Compliance Calendar tells them what’s theirs and when. The register stays current because the people who own the risks can update it without a specialist in the room.
Frequently Asked Questions

Most questions about the platform itself come down to trust and fit: where your data lives, how de.iterate connects to what you already run, and what happens when you need help. The answers below cover the detail, from hosting to sign-on to the people on the other end of the chat.

What is GRC software?

GRC stands for governance, risk and compliance. GRC software brings your policies, risks, controls, audits and evidence together, so you can run your compliance program and prove it's working.

Who is de.iterate for?

de.iterate is for organisations of every size, from start-ups working towards their first certification to enterprises and government suppliers managing several frameworks at once.

Which frameworks does de.iterate support?

de.iterate supports more than 25, including ISO 27001, SOC 2, Essential Eight, ISO 42001, ISO 9001, ISO 14001, ISO 45001, NIST, GDPR and the Privacy Acts. See our Frameworks page for the full list.

How long does it take to get certified?

It depends on your organisation's size and starting point, but many organisations using de.iterate can be audit-ready in under 12 weeks.

Where is our data hosted?

With de.iterate, you choose Australia or the EU. Production, backups and disaster recovery all stay in your chosen jurisdiction.

Will someone help us get set up?

Yes. de.iterate's Aussie GRC experts run a guided onboarding program, and our Management System Migration Tool brings across your existing policies, registers and documents.

How is de.iterate priced?

de.iterate is priced monthly, based on the frameworks you need. Plans start at AUD $179 a month for Starter (Essential Eight, SMB1001, the Privacy Act, and Cyber Essentials), with Business at $2,100 and Enterprise pricing on application. See our Plans page for details.

Multiple compliance frameworks, without extra effort


With de.iterate, the complexity of managing multiple frameworks doesn’t translate into increased workload. Our unified platform serves as a central hub for overseeing all your compliance activities, whether you’re working with bespoke frameworks or seeking to meet the criteria of the most sought-after security and privacy standards and certifications.

ISO 27001

Information Security Management Systems

The international standard that sets out the requirements for data protection systems. It’s all about keeping data safe and secure.
ISO 9001

Quality Management Systems

This standard defines the requirements for quality management. It’s all about ensuring your business consistently delivers high-quality products and services.
ISO 45001

Occupational Health and Safety Management Systems

The standard that specifies the requirements for an effective OH&S management system. Create a safer, healthier workplace.
ISO 14001

Environmental Management Systems

The global standard for building EMS. It gives you a structure to identify environmental impacts, manage obligations, strengthen governance.

ISO 42001

Artificial Intelligence Management Systems

This standard specifies the requirements for managing AI systems responsibly and ethically. It helps ensure trustworthy development and use of AI.

SOC 2

System and Organisation Control 2

This specifies how organisations should manage their customer’s data. It is one of the most sought-after security framework for SaaS companies. 

Privacy Acts

Australia, New Zealand, Canada, France, Italy, US and UK

Country-specific legislative frameworks established to protect individuals’ personal information from misuse, interference, unauthorised access, modification, and disclosure.

RRFR

Right Fit for Risk

The Australian Government’s Department of Employment and Workplace Relations uses the External Systems Accreditation Framework and the RFFR approach to assess and accredit third party service providers and systems.

DISP

Defence Industry Security Program

DISP is a critical initiative that ensures businesses in the defence supply chain meet stringent security requirements. DISP compliance is essential for companies that engage in Defence tenders, contracts and projects.

Simple monthly pricing, based on the frameworks you need

de.iterate pricing is structured around the compliance frameworks you choose to access, giving you the flexibility to build a program that fits your organisation’s needs. Every plan includes access to the de.iterate platform and its feature set, from automated and expert-led onboarding, through to migration support, assurance workflows, live registers, compliance reporting and the core documentation needed to run and maintain your management system with confidence.

AUD
GBP
Starter (per month)

$179£100

  • Essential Eight

  • SMB 1001

  • Privacy Acts

  • DISP

  • Cyber Essentials

Business (per month)

$2,100£1,250

  • ISO 27001

  • ISO 27701

  • ISO 42001

  • ISO 9001

  • ISO 45001

  • ISO 14001

  • SOC 2

  • NIST CSF 2.0

  • NIST 800-53

  • NIST 800-172

  • NIST 800-172

  • GDPR

  • Essential Eight

  • SMB 1001

  • Privacy Acts

  • DISP

  • Cyber Essentials

  • DORA

  • NIS2

  • CIS v8

  • EU AI Act

  • TISAX

Enterprise (per month)

$3,500£2,000

  • ISO 27001

  • ISO 27701

  • ISO 42001

  • ISO 9001

  • ISO 45001

  • ISO 14001

  • SOC 2

  • NIST CSF 2.0

  • NIST 800-53

  • NIST 800-171

  • NIST 800-172

  • GDPR

  • Essential Eight

  • SMB 1001

  • Privacy Acts

  • DISP

  • ISM

  • SOCI

  • Right Fit for Risk (RFFR)

  • Cyber Essentials

  • DORA

  • NIS2

  • CIS c8

  • EU AI Act

  • TISAX

Ready for simple, stress-free compliance? Want help from real GRC experts?